

When a CRM, an ERP, an online store, and several automations share information, deciding which one is the source of truth is not enough. That decision can clarify where to look up a value, but it does not always determine who is allowed to change it, when they can do so, or what happens if another system has already updated it.
The problem surfaces in everyday operations: an integration imports an old address again, an automation replaces a manual correction, or two processes update an order status based on different interpretations. Preventing these issues requires defining responsibility boundaries for each data field and process, rather than granting unrestricted authority to an entire application.
The goal is to give every change an understandable rule: which system or person can write to the field, under what conditions, how exceptions are resolved, and what information is retained to review what happened.
Why a source of truth does not prevent every conflict
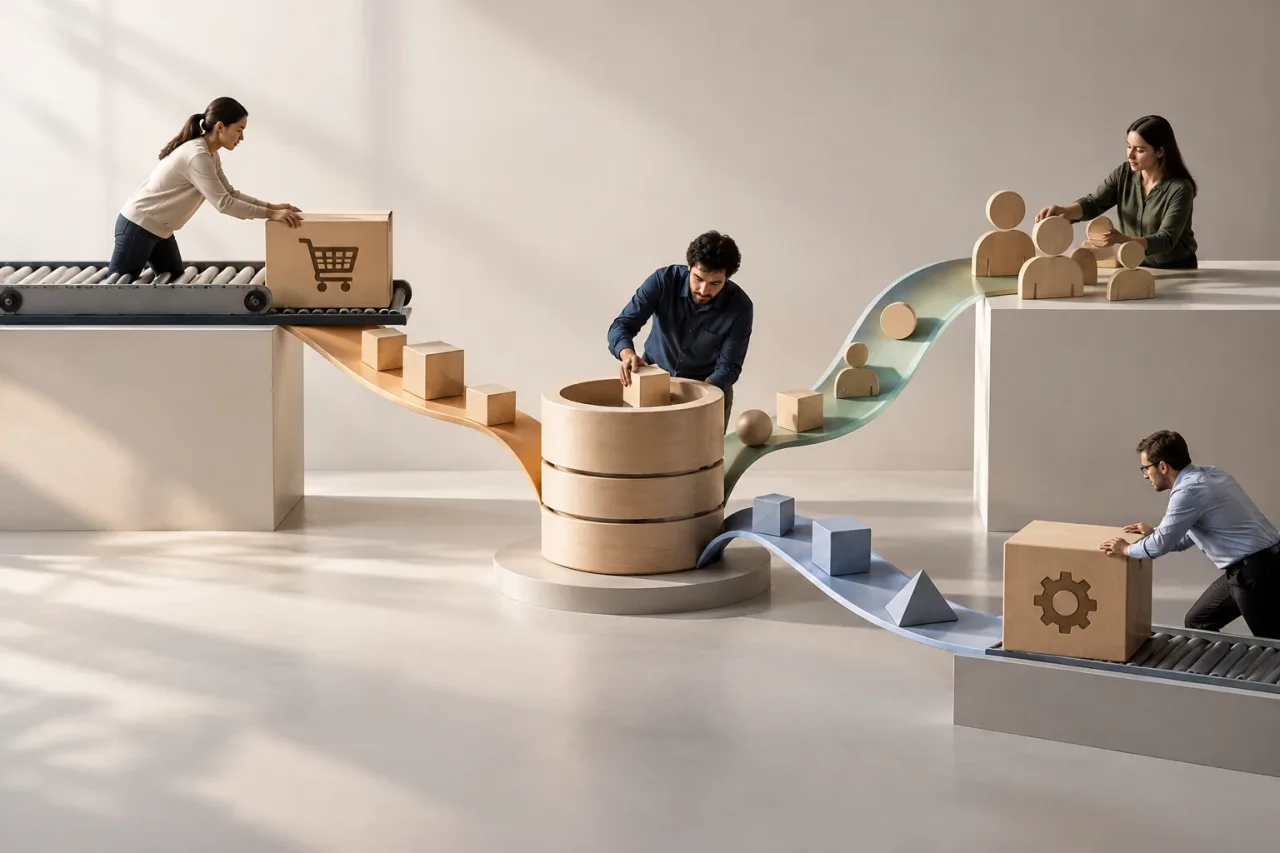
A source of truth identifies the reference point for a piece of data or a group of data. However, it may receive information from multiple systems without specifying which update should take precedence. Systems may also serve different purposes: an ecommerce platform records a request, the CRM manages the customer relationship, and the ERP handles billing.
It is therefore useful to separate three questions:
- Where is the official data consulted? This defines the reference that other processes should read.
- Who can modify it? This defines write authority, which may vary by field.
- Which version appears in each interface? This defines how the data is displayed, which does not necessarily mean the interface has permission to change it.
An application may display a shipping address and let someone edit it without being responsible for the billing address. Another system may receive the change and validate it before passing it on. Confusing these roles encourages overly broad rules such as “the CRM always wins,” even when the CRM did not originate the change.
Assigning authority by field and process stage
The practical unit of decision-making is not just the system: it is the field at a specific stage of the process. For example, a buyer may be able to edit a shipping address before an order is prepared, while the address may be locked once the package is being dispatched. Authority depends on context and timing, not just on the field name.
Document each important data point in a matrix that includes items such as:
- Field: The exact data point, with a shared definition and, if needed, its format.
- Write authority: The system, role, or process authorized to modify it.
- Condition: The stage, status, or validation required for a change to be accepted.
- Reader systems: The consumers that receive or display the value.
- Exceptions and resolution: What to do when there is a manual correction, a conflict, or invalid data.
- Record: The minimum information needed to reconstruct the change.
Start with fields that have the greatest operational impact: identifiers, order statuses, prices, billing details, addresses, and contact consent. You do not need to design an exhaustive policy for every minor field on day one. You do need to avoid ambiguity for fields whose modification could affect money, delivery, compliance, or customer service.
For each field, write a testable rule: “The ERP can update the billing status after validating payment; the ecommerce platform displays it but does not replace it.” If the rule includes vague phrases such as “usually” or “the most up-to-date system,” specify how that is determined.
Permissions, exceptions, and manual corrections
A good policy does not try to eliminate every exception. It defines who can authorize one and how consistency is maintained afterward. For example, a support team might correct a data point in response to a verified request; that authority should be limited by role, field, and process status. Giving the entire team or integration write permission turns an exception into a permanent source of conflict.
Before enabling a manual correction, decide:
- Which identity or role can make it and what checks are required.
- Which fields can be changed and which require approval.
- Whether the change is propagated automatically or needs review.
- Which systems must be updated and how a propagation failure is reported.
- What to do if the process has already advanced and the change is no longer safe.
It is also useful to distinguish the original value, the corrected value, and the reason for the intervention. If a manual edit cannot be propagated, do not discard it silently or mark the process as complete. Preserve the error status and assign someone to resolve it.
Resolving concurrent changes and late updates
Updates can arrive out of order: a slow connection delivers an old change after a newer one, or two systems modify the same field before either receives the other’s update. Automatically choosing “the last message received” can be wrong, because arrival order does not prove which change is valid.
Define a strategy that suits the level of risk:
- Single writer: Restrict modifications to one system or process. This is the simplest option when there is a clear owner and distributed editing is not needed.
- Status-based priority: Accept changes only at permitted stages. This is useful when authority passes from one process to another, such as when an order is confirmed or dispatched.
- Version control: Reject an update based on an older version or send it for review. This requires systems to compare a previous version or status.
- Supervised resolution: Record the conflict and request a human decision. This is appropriate when the cost of overwriting a valid value is greater than the cost of reviewing it.
A policy can combine methods. An address may accept customer changes before preparation and require intervention afterward. The important point is to define what happens when a condition fails: reject the change, leave it pending, raise an alert, or request approval. Avoid turning a conflict rule into a silent replacement.
Recording source and reason for diagnosis
When a value changes unexpectedly, the team needs to know who changed it, which system transmitted it, and which rule allowed the change to be accepted. As needed and as available, record the affected field, the old and new values, the timestamp, the source, the responsible identity or process, the validation result, and the reason, if one was provided.
This history is not just for investigating incidents. It helps identify integrations that resend outdated information, automations that write to fields at the wrong stage, and teams that frequently rely on exceptions. Define who can view these records and how long they are retained, based on operational needs and applicable obligations.
Checklist before activating an integration
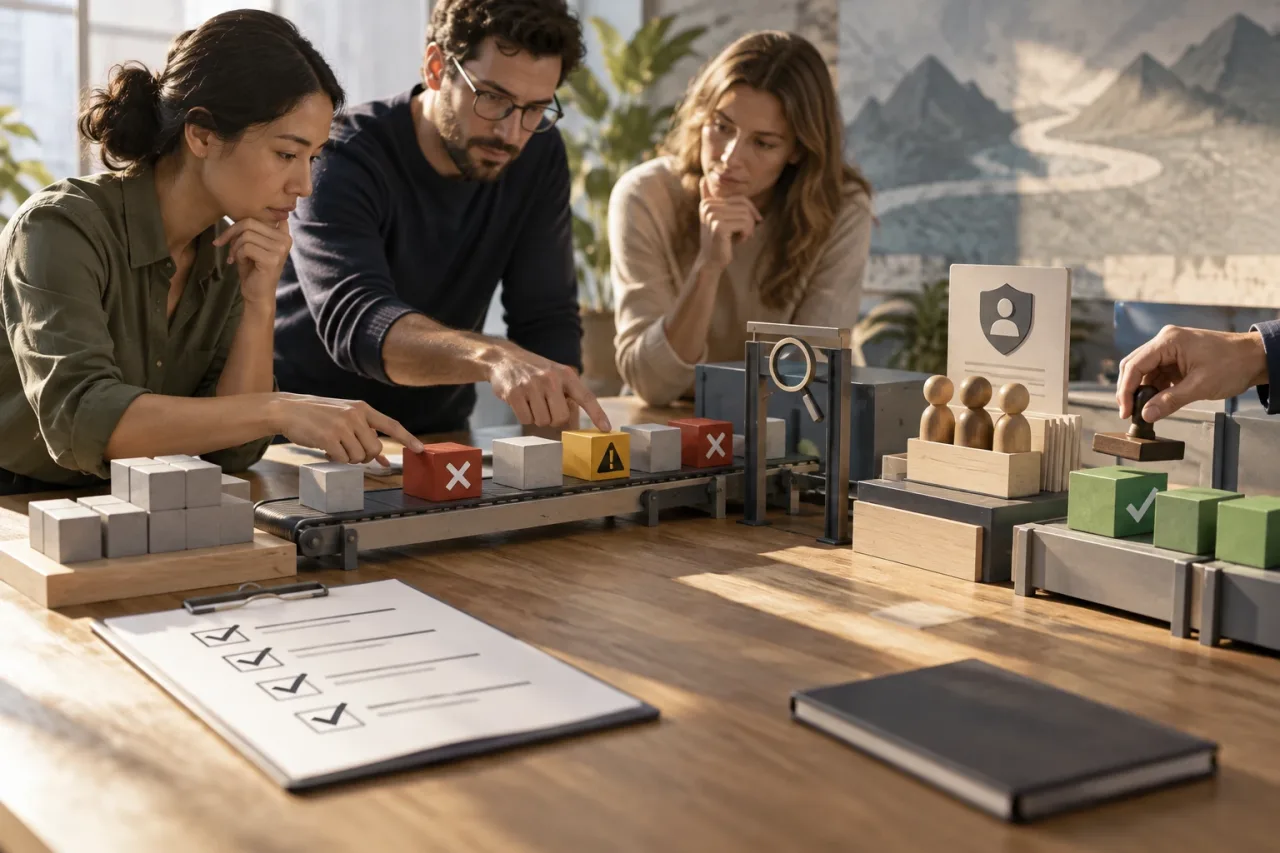
- Is each critical field and its meaning defined for all teams?
- Is the system that displays the data distinguished from the one authorized to modify it?
- Does the rule specify the writer, condition, and process stage?
- Are manual corrections, their owners, and their controls clearly defined?
- Is there a decision for duplicated or invalid data, and for updates received out of order?
- Do rejected or pending changes create a visible status and have an assigned owner?
- Can the source and reason for relevant changes be reconstructed?
- Is there a review process for updating the rules when systems or processes change?
Start with a pilot covering the highest-risk fields and monitor rejections, conflicts, and corrections. If a team needs to intervene repeatedly, review whether authority has been assigned to the wrong process or whether a documented exception is missing. The goal is not to prevent data from changing, but to ensure that every change has a defined authority, context, and consequence.