

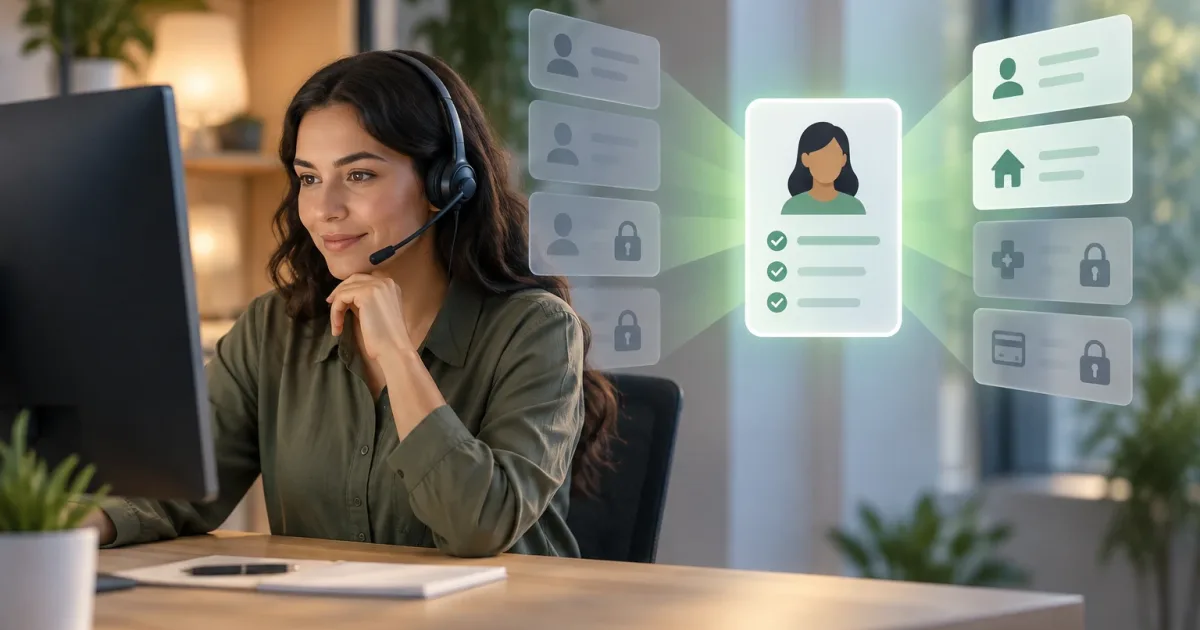
A support view can bring together data from a CRM, ecommerce platform, and other systems to help resolve customer inquiries. But just because information is available does not mean the entire team should always be able to see it. The design question is more specific: what does each person need to know to make the next decision on a case, and how can that information be provided with the least reasonable exposure?
Addressing this requires more than configuring general permissions. Data must be connected to tasks, its sensitivity classified, its presentation chosen, and exceptional situations considered. This framework helps product, customer service, and technology leaders design a useful view without turning it into a broad copy of connected systems.
Start with agent decisions, not available fields
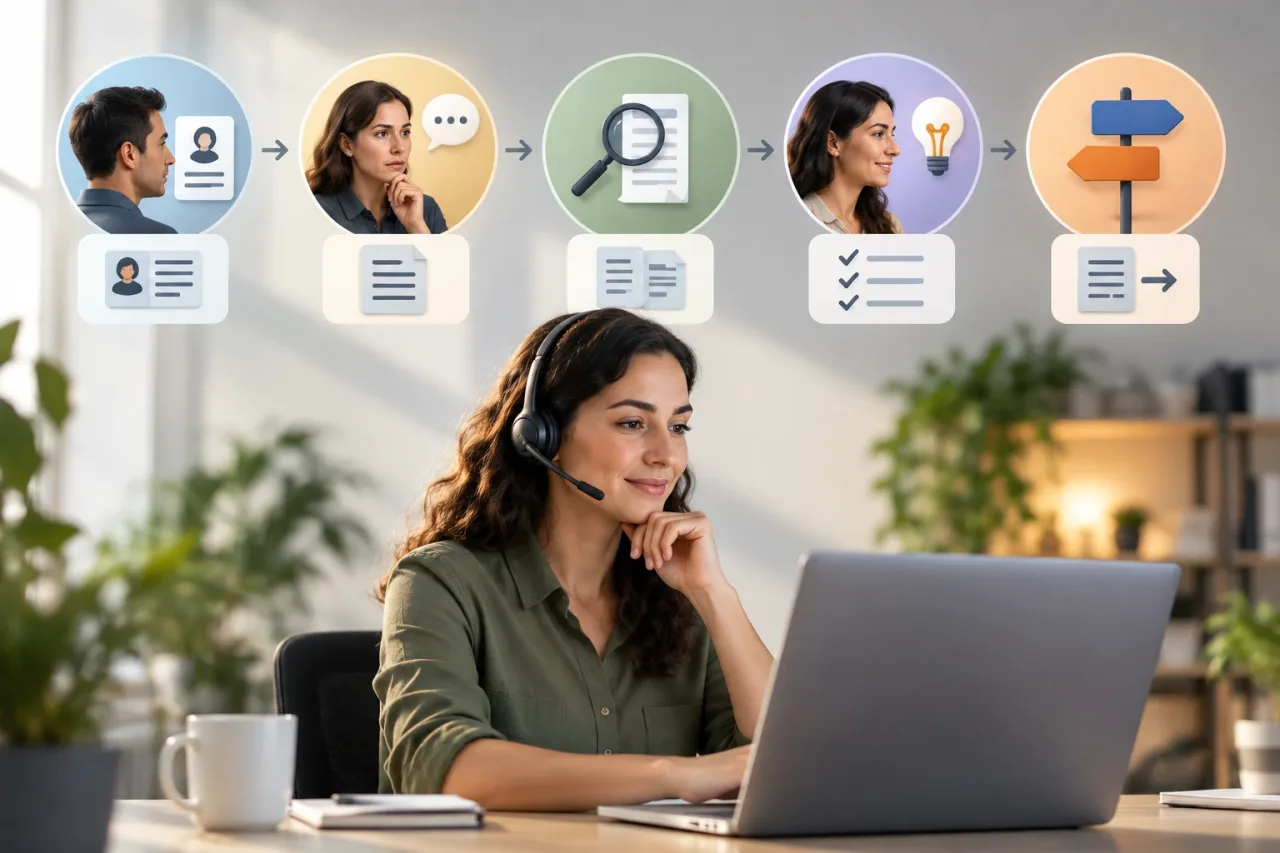
Begin by describing the typical stages of customer service: identify the customer, understand the reason for contact, verify a transaction, propose a solution, and close or escalate the case. For each stage, specify the decision the agent must make and the evidence needed to make it correctly.
For example, responding to a question about an order may require only an identifier, date, preparation status, and delivery information. Showing the buyer’s entire profile will not necessarily improve that decision. For a payment dispute, however, the agent may need to see the transaction status and relevant history, but not the full payment method details.
Document these needs in a simple table: case type, role, decision, required data, and permitted action. Distinguish between viewing data, editing it, exporting it, and taking an action. These are different capabilities and should not be bundled under a single “access” permission.
Classify data by usefulness, sensitivity, and necessity
Inventory the data that could appear in the view and assess each item from three perspectives:
- Usefulness: Does it change the response, priority, or next step?
- Sensitivity: Could it cause harm, reveal private information, or enable misuse if exposed unnecessarily?
- Necessity: Should it remain visible, be available only in certain cases, or not be shown to the agent?
The classification should reflect the organization’s context and applicable obligations; labeling an entire source as “sensitive” or “internal” is not enough. One contact detail may be needed to verify a request, while another profile attribute adds nothing to that case.
A practical approach is to assign each field a disposition: visible in the summary, available on demand, hidden from that role, or accessible only through an exception process. If a data item has no clear purpose in customer service, the default should be to leave it out of the view.
Choose between summaries, targeted retrieval, and restricted access
Not all data needs to be presented in the same way. A summary immediately provides frequently needed information, such as a transaction’s status. Targeted retrieval lets an agent access less frequently needed information when a case requires it, without keeping it permanently in view. Restricted access reserves more sensitive information for authorized roles or specific tasks.
Targeted retrieval does not replace permissions: the system must still verify that the user can view the data and that there is an operational reason to do so. If an exception is available, define who can request it, who approves it where applicable, how long it remains in effect, and how it is logged. Avoid creating an exception-access button that works as a permanent shortcut.
It is also worth presenting data at the minimum level of detail needed to complete the task. For example, showing part of an identifier may help an agent recognize a transaction without exposing the full value. Data minimization must still support verification; if the agent needs to confirm information, design a clear method that does not require them to reveal data to the customer during the process.
Design permissions by role, case, and relationship
Role-based permissions are a starting point, but they may not be sufficient on their own. Two agents with the same job title may handle different products, regions, or case types. Define understandable rules that combine role with task type and the agent’s relationship to the case or customer where appropriate.
For each permission, specify its scope and action: which data categories can be accessed, in which cases, and whether editing or exporting is allowed. Also consider the access lifecycle: role changes, temporary cover, escalations, and the end of the agent’s relationship to a case. A rule that does not account for these changes can leave access broader than necessary.
Test the rules with concrete examples, including negative cases: an agent searching for a customer without an assigned request, someone moving to another team, or a person trying to access an escalated case. The system’s response should be consistent and clear, without revealing additional details in error messages.
Connect systems without creating unnecessary copies
When the view combines a CRM, ecommerce platform, and other services, decide which system is the source of record for each data item and how it will be retrieved. Where feasible, retrieve the necessary information from its source system rather than copying complete profiles into a parallel database. A copy can become outdated or retain information after it is no longer needed for the task.
The integration should also define what happens if a system does not respond, returns incomplete data, or presents contradictory statuses. Do not turn a connection error into implied authorization to show more information from another source. Tell the agent which data could not be verified and what operational alternative is available, such as trying again or escalating the case.
In the interface, identify the data source and how current the information is when that matters to the decision. Avoid combining values from different systems as if they represented a single source of truth. The goal is to provide reliable context, not to add fields simply because they can be connected.
Log access and changes for a clear purpose
Auditability makes it possible to review who viewed or changed information and in what context. Determine which events are needed to investigate incidents and oversee use: depending on the design and applicable obligations, relevant elements may include the user, time, resource, action, and outcome. Log exception-based queries too if they are part of the access model.
Logging should be proportionate. Including the full contents of sensitive data in every event can create a new exposure. Keep the metadata needed for review and define who can access the logs, how long they are retained, and what process applies. Ensure that auditability also covers actions performed through integrations if those actions are part of the operation to be audited.
Validate the view against routine cases and exceptions
Before implementing the design, walk through it with agents and customer service leads. Simulate common inquiries, a dispute, an escalation, and an integration failure. Check whether agents can resolve each case without requesting excessive access and whether they understand why data is hidden or out of date.
After launch, also review diagnostic signals: repeated requests for exceptional access may indicate that the view omits necessary context; queries for fields that rarely affect a resolution may suggest unnecessary exposure. Interpret these signals alongside response quality and team procedures: on their own, they do not prove that permissions are right or wrong.
Pre-implementation checklist
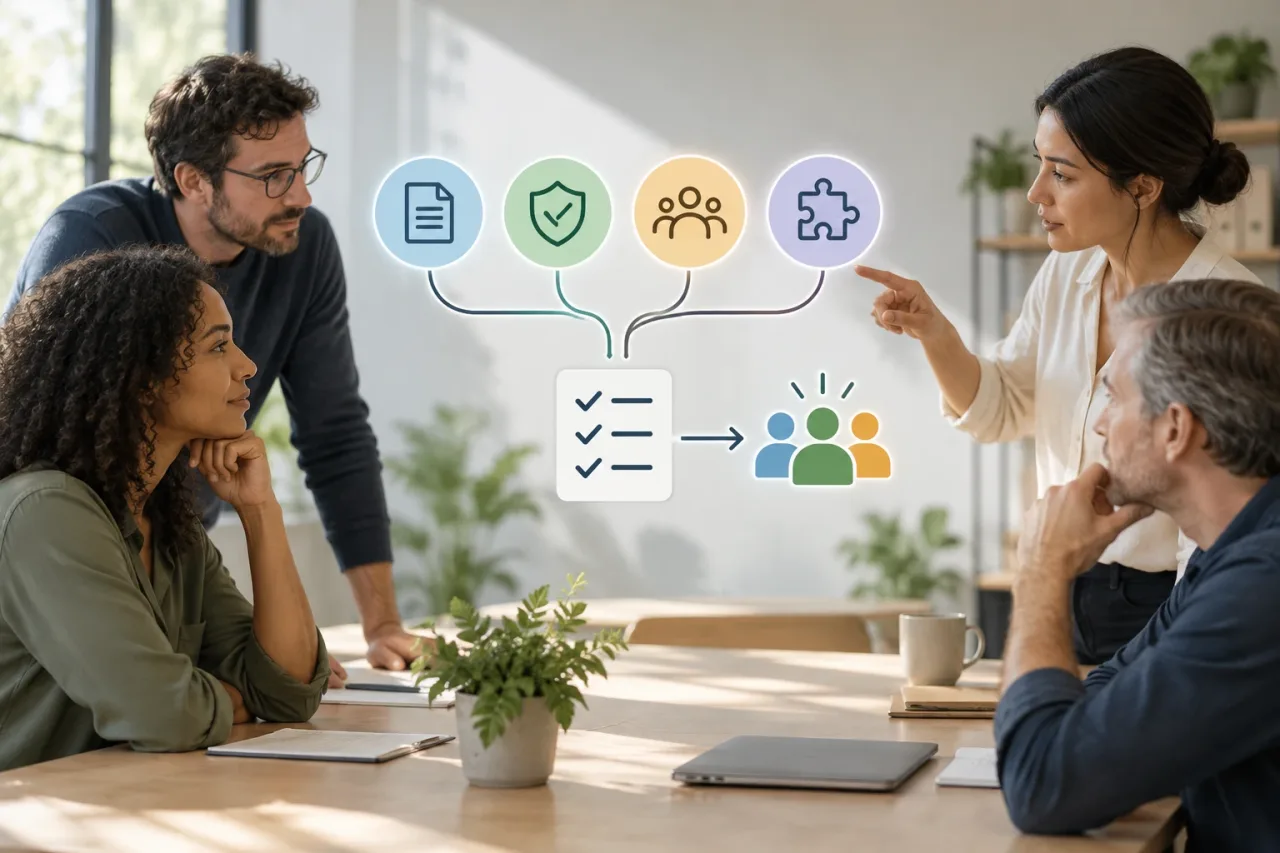
- Is every visible data item tied to a specific customer service decision?
- Are viewing, editing, exporting, and acting on information treated as separate capabilities?
- Is more sensitive data hidden, summarized, or subject to a specific need?
- Do permissions account for role, task, and relationship to the case?
- Do exceptions have a reason, defined scope, and audit trail?
- Is it clear which system is the source of record and what happens if it fails?
- Can logs support access reviews without unnecessarily duplicating sensitive data?
- Have routine, negative, and exceptional scenarios been tested with the support team?
The central principle is simple: show what is needed to resolve the case, at the right time and to the right person. Applying it requires explicit decisions about usefulness, sensitivity, permissions, and integration. This gives the team actionable context without assuming that greater visibility means better customer service.