A field such as status = "pending" seems sufficient until a process accumulates approvals, exceptions, and actions that depend on how it reached that point. Then practical questions arise: Can it be canceled after approval? Who can reopen a case? What happens if the same request arrives twice? A state machine helps answer them by describing not just the current state, but also the permitted changes and their effects.
Not every workflow needs this model. For a short, linear process, a status label and a few simple rules may be easier to build and maintain. The decision is about comparing the workflow’s actual complexity with the cost of making its rules explicit—not adopting a pattern in advance.
Status Labels and State Machines: What Changes?
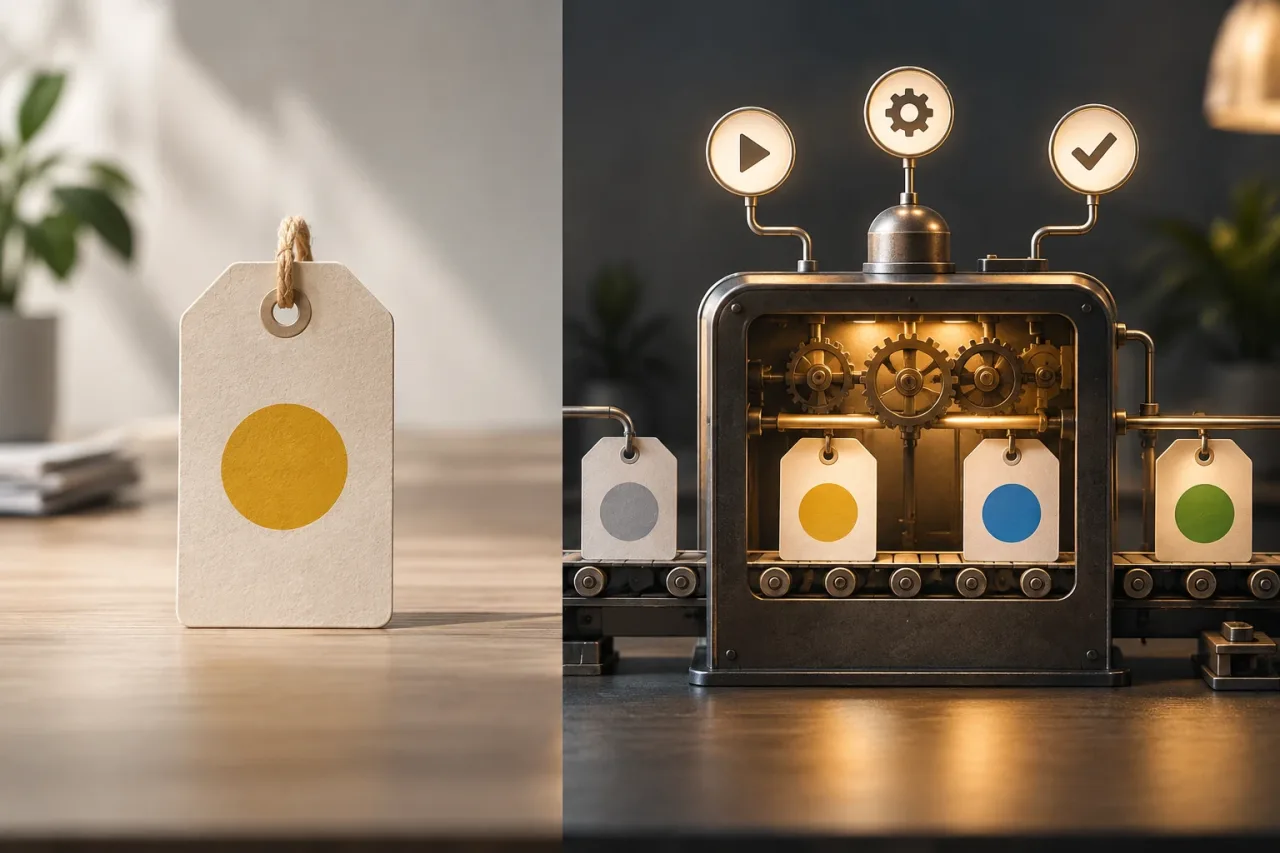
Storing a status as a label represents a current condition: for example, a task can be marked “pending” or “completed.” On its own, that label does not explain which changes are valid, what event triggers them, or what actions should accompany them. That logic is often spread across the interface, the server, and different conditions in the code.
A state machine describes a process as a defined set of states and transitions. A transition specifies which event allows a change from one state to another and, where applicable, which conditions must be met or which actions are performed. The current state therefore limits the possible next steps.
The difference is not the number of labels in a database. A status field can be part of an explicit state machine if the system validates transitions. And a long list of states is not a good model by itself if nobody can explain how the process moves between them.
Signs That Explicit Transitions Are Worth Defining
The model starts to add value when rules depend on the point in the process and transition errors have consequences. Look for these signs:
- Different permitted actions: Not everyone can approve, edit, or cancel at every stage, or an action is available only after validation.
- Alternative paths: A request may be approved, rejected, returned for more information, or canceled.
- Distributed rules: Different parts of the application independently check whether an operation is valid, creating a risk of conflicting decisions.
- Effects associated with a change: A transition must record a decision, notify someone, or start another task. It helps to distinguish this effect from a simple change of label.
- Retries and concurrency: Two people or processes might try to modify the same case, or an integration might send the same event more than once.
A useful diagnostic sign is that the team often debates whether a change “should be allowed” at a particular stage. If the answer depends on the previous state, who is acting, or a business outcome, it is worth recording the rule explicitly in one place.
When Simple States Are Enough
A simple model is often sufficient when the process is linear, has few transitions, and has exceptions that are rare or easy to handle. For example, an internal task that moves from “pending” to “completed” may need only a field and a clear check, especially if there are no approvals, retries, or external consequences.
Operational cost matters too. A state machine introduces concepts, tests, and maintenance. If the workflow is unambiguous, that cost may outweigh the benefit. Do not turn every screen change, interface step, or minor variation into a business state: a visual experience does not always correspond to a stage in the process.
As a practical rule, start with the simplest representation that enforces the important rules. If repeated conditions, implicit transitions, or incidents caused by invalid changes begin to appear, review the design. You can evolve it gradually: there is no need to redesign the entire process just to formalize the highest-risk transitions first.
Criteria for Making the Decision
There is no universal number of states or transitions at which a state machine becomes necessary. Assess the workflow’s behavior and the impact of errors by asking specific questions:
- How many real paths are there? Count business paths and their branches, not just labels. Several paths with different permissions or outcomes often justify an explicit model.
- What happens if someone attempts an invalid transition? If the effect is a reversible inconvenience, simple validation may be enough. If it could cause an incorrect decision, duplicated work, or an action that is difficult to undo, define clearer controls.
- Can changes happen simultaneously, or can events repeat? If so, establish how to check that the state has not changed since the operation began and how to prevent processing the same event twice from duplicating its effects.
- Does the process need to be explainable? If support, audit, or operations teams need to know who did what, when, and why, separating the current state from the event history makes it easier to reconstruct how the process evolved.
- Can the rules fit in one understandable place? If they require chained exceptions across several components, the problem is no longer just the number of states: it suggests the workflow lacks a single definition.
How to Name States, Events, and Exceptions
Use terms that describe stages the business can recognize. A state answers “What situation is the case in?”; an event answers “What happened to change it?” For example, “under review” can be a state and “review approved” an event. Avoid treating the two concepts as interchangeable.
Also separate the stage from the outcome when they are different dimensions. “Closed” describes a final stage, while “approved” or “rejected” describes an outcome. If they are combined, you may end up with compound states such as “closed and rejected,” multiplying the variations and making the rules harder to reason about.
Mark which states are terminal—that is, where the process normally ends. Separately define whether cancellation or reopening is possible and who can do it. A terminal state does not have to prevent every administrative action, but the exception should be bounded and should not become a back door for bypassing the rules.
For retries, avoid creating a new state for every attempt if the case remains at the same stage. Keep the appropriate state and record the attempt in the history or as a separate piece of data. Apply the same principle to failures and exceptions: create a distinct state only if it meaningfully changes what the business can do next.
Hypothetical Example: A Request Under Review
Imagine a request that is received, reviewed, and ultimately approved or rejected. In the simplest version, its states might be “received,” “under review,” and “resolved,” with an outcome recorded separately. If the team needs to request additional information, the workflow must represent that pause and define which event allows the case to return to review when a response arrives.
A transition can specify that only an authorized person may approve or reject a case in the “under review” state. If it is rejected, the case becomes resolved with the outcome “rejected”; if information is missing, it moves to “awaiting information.” A state machine does not require a special platform: it is enough for the system to validate those changes consistently and record the necessary data.
This example is hypothetical; names and rules should be adapted to the actual process. If requesting information does not change the available actions or require follow-up, recording a note may be enough. The model should reflect operational differences, not anticipate every imaginable possibility.
Common Mistakes and a Checklist
A model can become more complicated than the process if it creates states for every detail, mixes permissions with stages, or fails to define what happens to existing cases when the rules change. It is also a mistake to model transitions in a diagram but let the code ignore them: the rule must be enforced wherever the change is accepted.
Before choosing or reviewing an approach, check the following:
- Does each state represent a situation the business can explain?
- Do events describe what happened, and do transitions specify which changes are permitted?
- Are alternative paths, cancellations, and reopenings clearly defined?
- Are invalid operations rejected, and are repeated events or simultaneous changes handled?
- Is history recorded when decisions need to be reconstructed?
- Are there states that can be merged without losing important rules or information?
Choose a state machine when it makes rules explicit and enforceable that would otherwise be scattered, and when the cost of an incorrect transition justifies that control. If the process is linear and predictable, start with simple states. Review the decision when paths, exceptions, or consequences change: the best model is the simplest one that faithfully represents how the work evolves.