

Choosing how to store each customer’s data is an architectural decision with consequences for security, operations, and product evolution. In a multi-tenant SaaS, giving each user a different interface is not enough: the system must control which data each customer can read and modify, including in the event of code errors, background jobs, or configuration changes.
There is no universally best model. A shared database can simplify operations, while a dedicated database may help meet certain isolation requirements, but it also multiplies operational tasks and costs. The right choice depends on the risks you want to reduce, your commitments to customers, and your team’s actual capacity to operate the architecture.
What data isolation per customer means
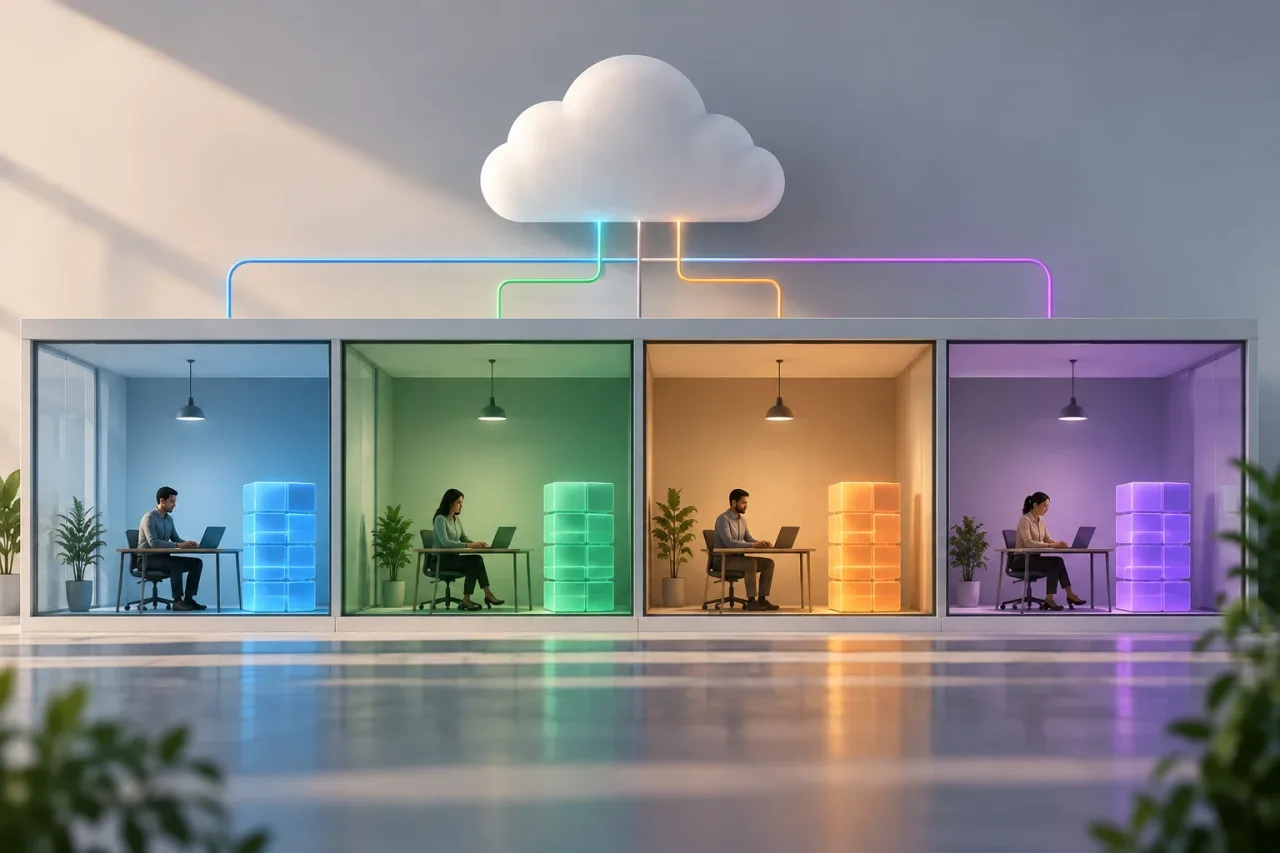
Data isolation, or multitenancy, means logically separating each organization’s information within a shared service. A tenant is usually a customer company, although the business model may define a different unit. The application must associate every request, process, and data item with an authorized tenant, and enforce that relationship consistently.
Separating storage does not automatically eliminate every risk. Incorrect authorization can let a user access another customer’s features; an exported log or analytics system can expose data even if the primary database is properly segmented. Backups, logs, caches, files, integrations, and support environments must also be considered.
That is why the useful question is not just where to store the data, but what controls prevent cross-customer access and how you verify that they work. Storage architecture is one layer of that strategy, not a substitute for authentication, authorization, code review, or secure operational practices.
Three common storage models
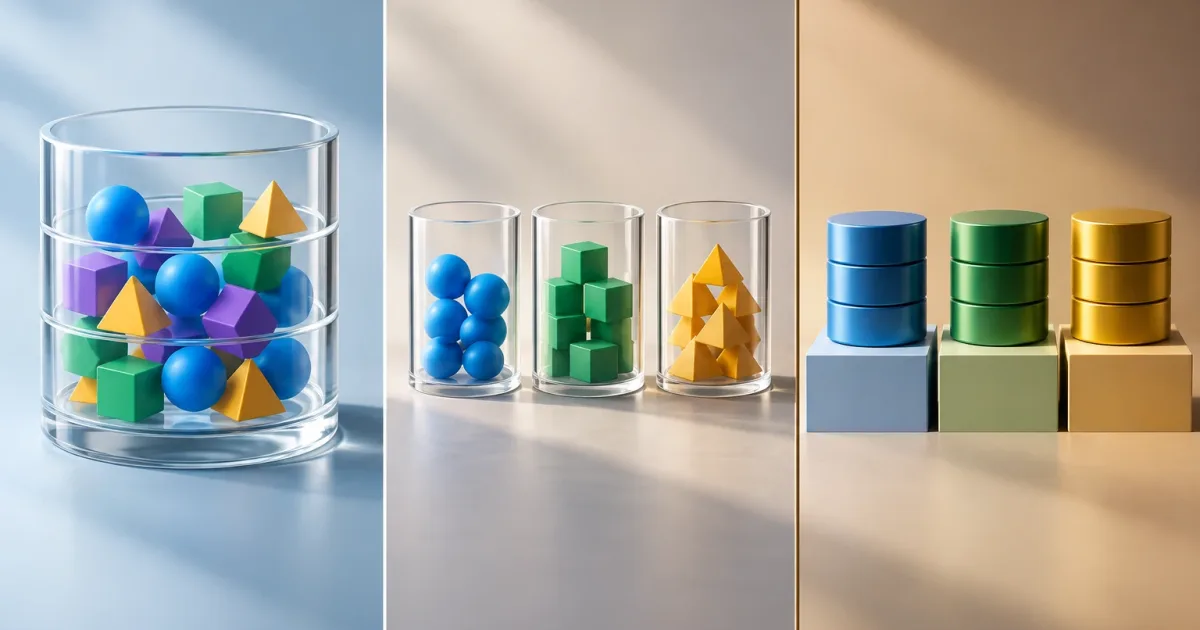
Shared database
All customers use the same database and often the same tables. Each record includes a tenant identifier, and queries must filter by it. This model usually reduces provisioning complexity and makes it easier to apply schema changes once. It can be a reasonable option when the product is new, customer requirements are similar, and the team can establish reliable controls.
Its main risk is that a query or process may omit the filter. The result could be data read or modified across customers. Customers also share resources: heavy usage by one company can affect others if capacity is not managed.
Separate schema per customer
One database hosts multiple schemas, one per customer, with similar tables. This separation can make the boundary between datasets more visible and support certain customer-specific operations. However, it does not eliminate routing errors or guarantee resource isolation. Migrations and tools must handle schemas consistently; with many customers, managing versions and exceptions can become difficult.
Dedicated database
Each customer, or a small group of customers, has its own database. This can make data placement and selective restores easier, and help meet contractual requirements for distinct resources or access boundaries. Depending on how services are deployed, it can also reduce the impact of heavy usage or an incident on other customers.
The trade-off is operational: provisioning, updating, monitoring, backing up, and testing many databases requires automation and team capacity. A dedicated database also does not protect against excessive permissions, compromised credentials, or application errors. Verify what isolation the chosen platform actually provides.
Criteria for making a decision
Evaluate the models against your product’s specific requirements, rather than an abstract preference for separation. Document both current needs and commitments that are likely to affect future development.
- Risk of cross-customer access: identify sensitive data, who can access it, and where tenant context could be lost. Define preventive controls and negative tests that attempt to access another customer’s data.
- Customer requirements: check contractual obligations and needs related to residency, retention, restoration, or auditing. Do not treat a request for a “dedicated database” as a legal requirement without validating it with the responsible teams.
- Operations: estimate the work involved in deployments, backups, restores, observability, support, and incident management. Consider whether the team can automate these tasks repeatably.
- Product variability: customers with very different versions, extensions, or policies may need clearer boundaries. Even so, avoiding a common platform can create divergences that are difficult to maintain.
- Cost of change: consider how you would move a customer, validate the transferred data, and estimate how long a transition might take. A simple initial decision is safer if it does not block future alternatives.
A decision matrix helps make trade-offs explicit. Score each option against verifiable requirements, and distinguish mandatory criteria from preferences. If a customer requires something a shared model cannot deliver, that constraint should outweigh a general preference for simplicity.
Controls for a shared model
If you choose a shared database, treat the tenant identifier as an essential part of the design. It should come from an identity and context validated by the server, not from an arbitrary value sent by the browser. Data access layers should receive that context consistently and prevent queries from running without tenant scope.
Where the technology allows, establish controls at more than one layer: database constraints, limited permissions, access policies, and application-level validation. Do not treat these controls as interchangeable; verify which ones apply to your processes, connections, and administrative tasks. For asynchronous processes, queues, and scheduled tasks, pass and validate the tenant explicitly.
Include automated tests that create at least two tenants and check reads, writes, searches, exports, and support operations. Add reviews for new queries and monitor signals such as authorization errors, queries without context, and failed jobs. Logs should help investigate incidents without exposing unnecessary sensitive data.
When to adopt a hybrid approach
A hybrid model uses a shared database for most customers and separate storage for those with a justified need. It can be useful when there is a demonstrable difference in requirements, volume, residency, or isolation. It also lets you start with shared operations and reserve dedicated resources where they provide value.
Define allocation rules before making exceptions: which requirement qualifies a customer for a dedicated database, who approves the change, how costs are calculated, and what support is provided. Maintain a common mechanism for identifying each tenant’s location, and keep business logic independent of database names or addresses. Without clear criteria, a hybrid approach becomes a collection of special cases.
Design for migration and make the decision revisable
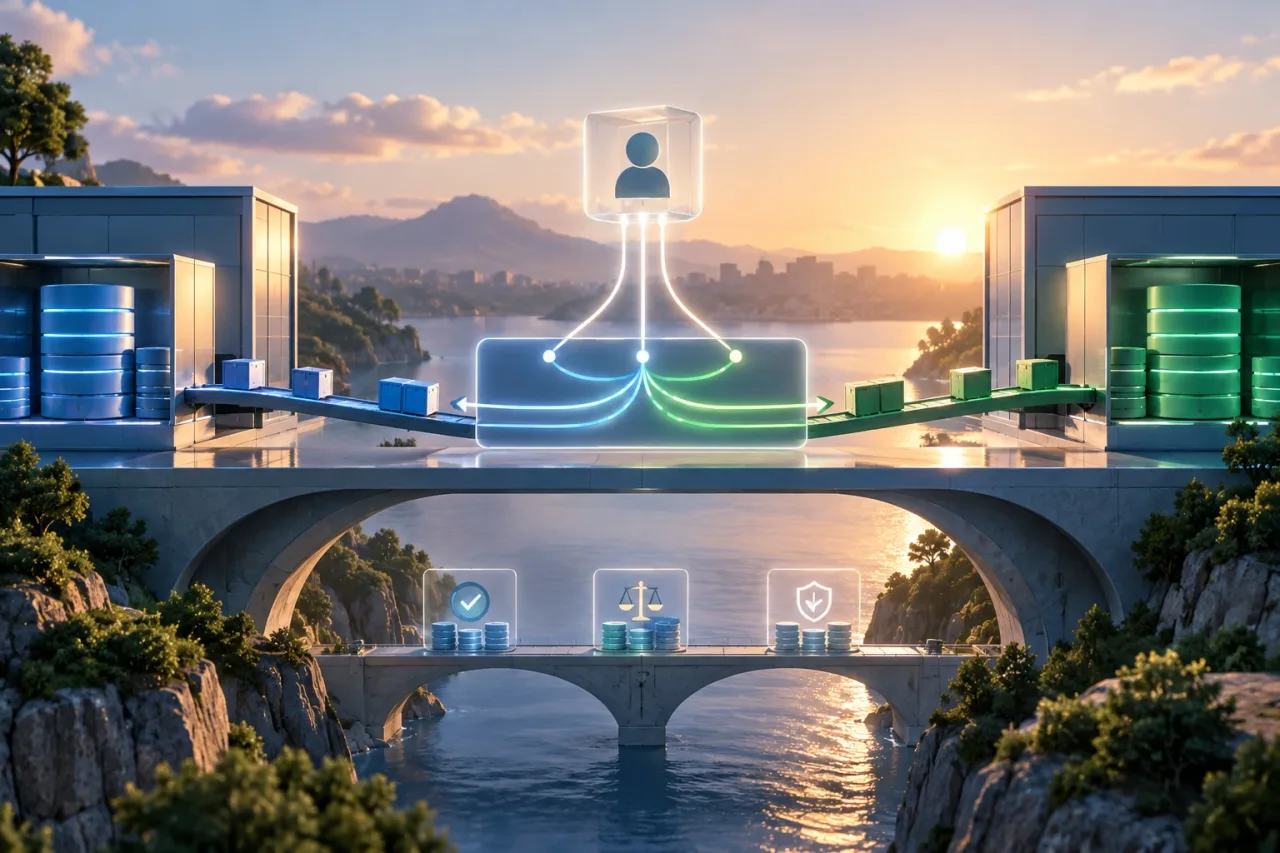
From the start, separate tenant identity from physical location. Use an access layer that can route operations to the right store, and automate provisioning and migrations. Where possible, keep schema changes compatible during transitions, and define how to verify record counts, integrity, and permissions before enabling the destination.
A migration may involve copying data, stopping writes, or synchronizing changes before switching routing. The procedure depends on the technology and continuity requirements: rehearse it, define a rollback strategy, and communicate the expected impact. Do not assume that moving to a dedicated database is always simpler; volume, dependencies, and consistency determine the difficulty.
Before finalizing the decision, answer these questions in writing:
- What unit represents a tenant, and where does its context come from?
- Which requirements are mandatory, and which are negotiable preferences?
- What controls detect and block access between customers?
- Who operates backups, restores, deployments, and exceptions?
- What signals would justify changing models, and how would the migration be carried out?
Choose the model that meets your requirements with an operating burden your team can sustain. Revisit the decision as customers, risks, or platform capabilities change. The right isolation model is not the most complex one: it is the one with verifiable controls that can be operated consistently.