

Many teams respond to the need to “know what happened” with a single solution: storing every change, access, error, and message in the same table or logging tool. The result is usually predictable: too much data to investigate an incident, insufficient evidence for a review, and unnecessary exposure of sensitive information.
The right decision is not how much to record, but which question the process must be able to answer, for whom, and with what consequence. A user who wants to recover the status of their request, a support team investigating an integration failure, and a person reviewing a disputed approval need different information. Their records should also have different purposes, permissions, levels of detail, and retention periods.
Separating functional history, audit trails, and operational traceability makes it possible to design explainable processes without turning every system into an indiscriminate data repository. This guide provides criteria for choosing each mechanism and combining them when the workflow genuinely requires it.
Three needs that are often confused, but are not equivalent
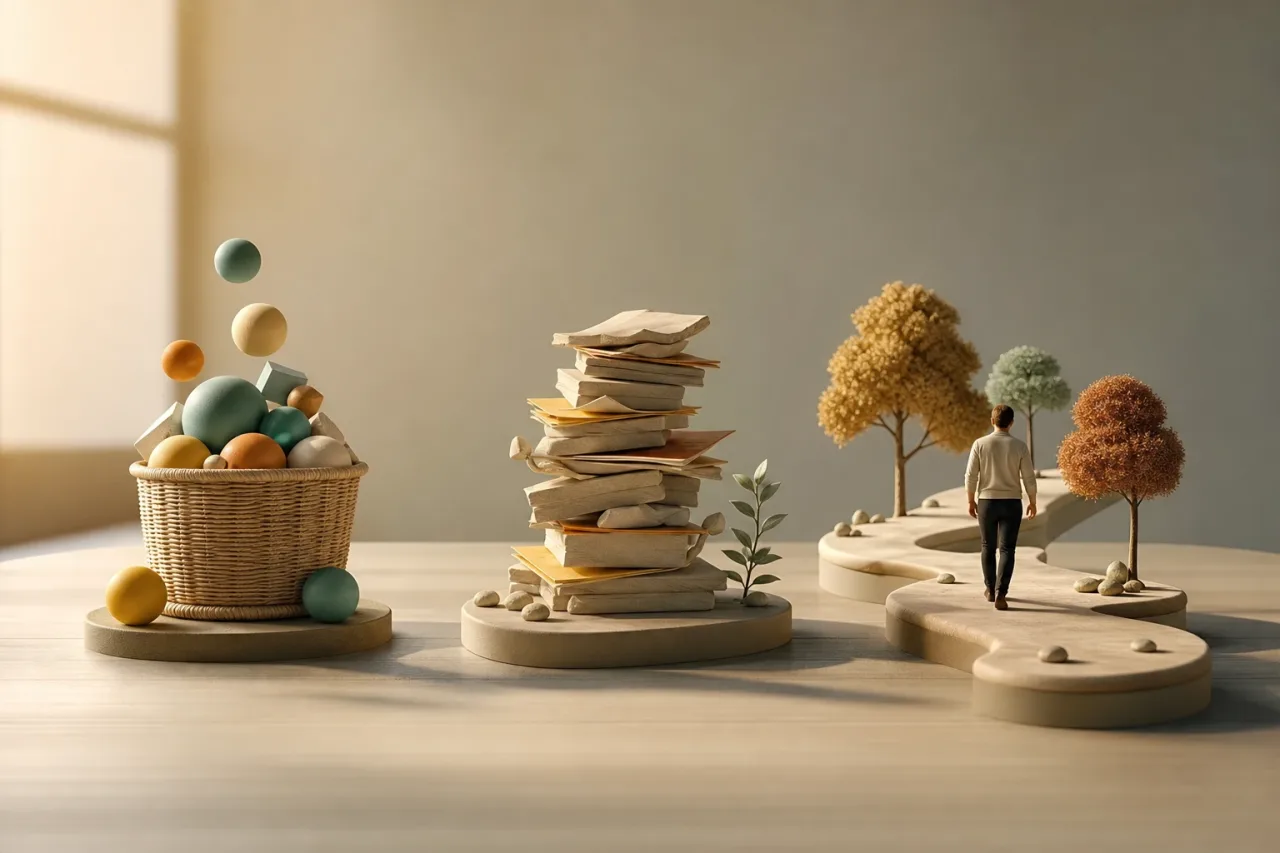
Functional history preserves the evolution that matters for using the product or managing a case. For example, the statuses of a request, review comments, versions of a proposal, or the reason a case was returned. Its purpose is to provide operational continuity for users and internal teams.
An audit trail provides evidence of significant actions: who did what, when, to which object, and from which available context. It is needed when an action has control, authorization, security, internal compliance, or accountability consequences. It should not depend on the product’s current screen still retaining the data or on the user being able to edit it later.
Operational traceability makes it possible to follow a technical or distributed process in order to diagnose its execution. It connects a request with its service calls, queues, synchronizations, retries, responses, and errors. It helps explain where a workflow was interrupted, how long it took, and which component needs attention.
- History answers: how has this case evolved?
- Auditing answers: what significant action occurred, and who was responsible?
- Traceability answers: where did the execution go, and where did it fail?
A single event may feed all three mechanisms, but they should not be indistinguishable copies. An approval may appear in the history as a visible milestone, generate an audit entry with the approver and decision, and carry a correlation identifier to trace subsequent communication with other systems.
Start with the questions and the consequences
Before defining fields or tools, list the facts that the process must be able to reconstruct. Then assign each fact to a specific need. This sequence avoids the common mistake of adopting the technical log format as a universal record.
- Define the case or unit of analysis. It may be a request, order, account, approval, or specific execution.
- State the future question. For example: “Why was it rejected?”, “Who changed the permission?”, or “Why was the notification not delivered?”
- Identify the impact of being unable to answer it. Distinguish operational inconvenience, loss of trust, security risk, conflict between teams, or inability to correct an error.
- Determine the authorized audience. The requester, support, operations, process owners, and technical teams do not need the same level of detail.
- Set the time horizon. The usefulness of a debugging identifier may last days; that of a decision may extend throughout the case lifecycle.
There are clear signs that auditing is needed: permission changes, approvals, delegations, document replacements, data exports, access to sensitive information, rule changes, and administrative operations. In these situations, being able to say that “the system shows the current state” is not enough. It is necessary to preserve the fact that an action occurred and the minimum context needed to evaluate it.
By contrast, if the goal is to handle a request or understand its normal evolution, functional history is usually sufficient. If the issue only appears across services or when handling retries, operational traceability is the priority.
What to record: a proportionate event model
The quality of a record does not increase simply by adding columns. A useful model captures the attributes needed to answer the intended question and excludes those that provide neither evidence nor diagnostic value.
Functional history events
Record milestones that explain the business journey: creation, submission, validation, return, approval, rejection, cancellation, closure, and communications relevant to the case. Include an understandable summary of the change and, when useful, the stated reason.
- Case identifier and previous and new status.
- Time of the milestone and visible actor, where applicable.
- Associated reason or comment.
- Reference to related documents, versions, or decisions.
Audit events
Record actions with impact, not every interface interaction. For each entry, retain the actor, action, affected object, time, outcome, and the context needed to interpret the fact. If a decision depends on a rule or external evidence, retain a verifiable reference to the applicable version, rather than necessarily keeping a complete copy of sensitive information.
- Creation, change, or removal of permissions and roles.
- Approval, rejection, delegation, or reversal of decisions.
- Changes to critical data, configuration, or rules.
- Access, download, export, or sharing involving sensitive information.
- Subsequent corrections that alter a decision or relevant data.
Operational traceability events
Connect components through a correlation identifier. Record the sending and receiving service, operation, timestamps, outcome, error code, number of retries, and a secure reference to the case. Avoid including complete request bodies, secrets, tokens, or personal data as a default practice.
correlation_id=8f31...
case_id=request-204
service=validation
operation=verify_data
result=error
retry=2
A practical rule: retain previous and subsequent values only when the value change is essential to explain a decision, resolve a dispute, or restore the state. For sensitive fields, it may be preferable to record that the field changed, its classification, and the reference to a protected version, rather than exposing the content in every event.
Immutability, corrections, and evidence quality
An audit trail loses value if someone can silently edit its entries. Auditable actions should be append-only: if there is an error, add a correction that references the original event, identifies the reason, and makes clear which interpretation is current. Do not erase the past to make it appear that it never existed.
This does not mean that every piece of data must be immutable. Functional history can be enriched with later information, such as an explanation or an updated document, as long as the design clearly distinguishes between the current state and milestones that have already occurred. Operational traceability, meanwhile, can accommodate more frequent data cleanup and automatic purging processes because its primary purpose is technical.
Also review the quality of the source. If an integration writes events asynchronously, there is a risk that the operation completes but the record is not generated, or that it appears twice after a retry. Design unique event identifiers, mark the source and write outcome, and treat repeated delivery as an expected scenario. The absence of a critical event should be detectable, not a suspicion that depends on manually reviewing several systems.
Queries, permissions, and retention: where design becomes useful
A record only adds value if it can be queried without exposing more than necessary. Design views around the work they need to support, not around how data was stored.
- Case view: a clear timeline to reconstruct functional evolution, using business language.
- Review view: auditable actions, actor, date, outcome, references, and relevant changes.
- Incident view: searches by correlation identifier, system, error, time range, and retries.
Separate read and administration permissions. A person operating a process may need to view the history of a request, but not the technical details of its integrations. The technical team may need execution metadata, but not the content of related documents. And people who administer the platform should not be able to alter audit records without that action itself being traceable.
Retention should be defined by record type. Keeping detailed traces indefinitely increases cost, noise, and exposure surface. Deleting approval evidence too soon leaves the process unable to explain itself. Document the purpose, owner, authorized access, review period, and deletion or anonymization criteria for each event class.
Example: a request with a form, approval, and integration
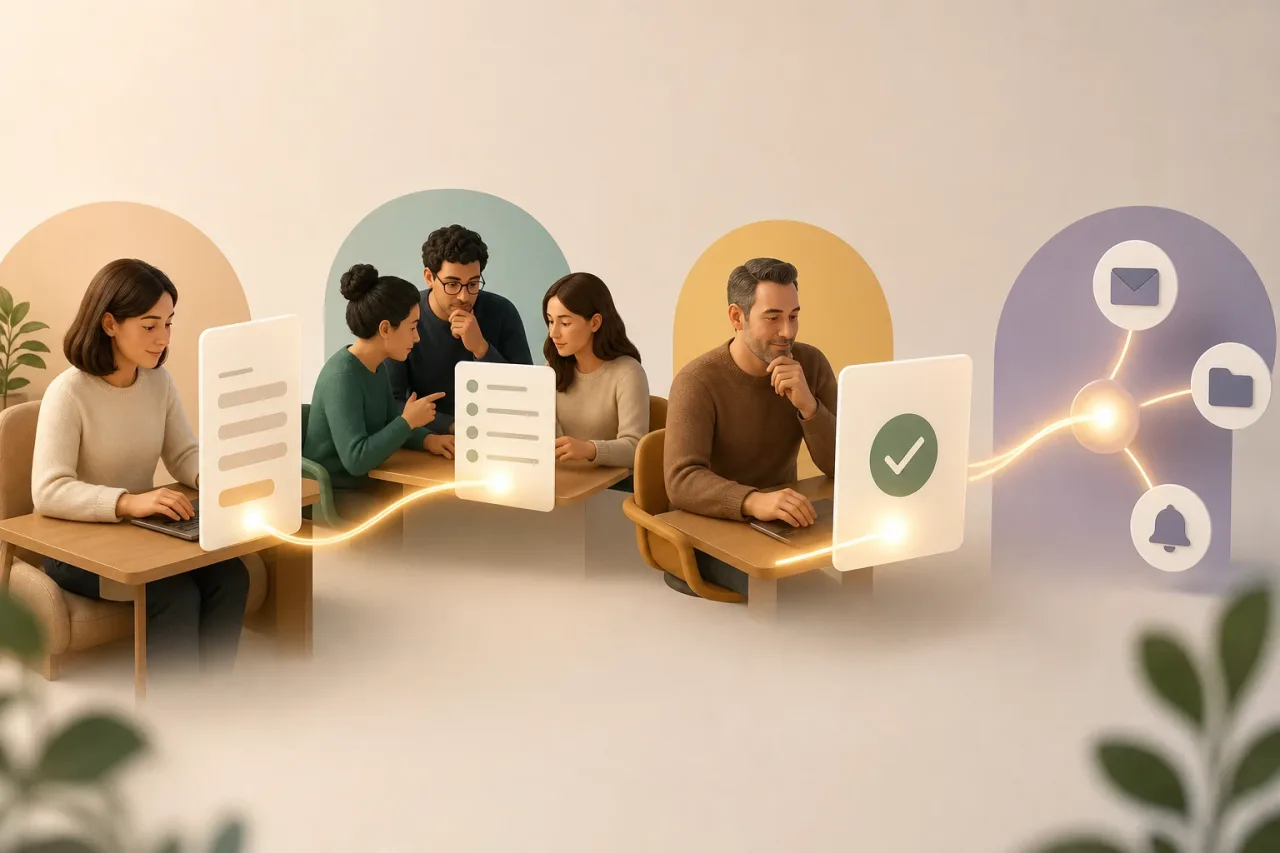
Imagine a request that someone starts in a form. A team validates it, a responsible person approves it, and the system communicates the outcome through an integration.
Functional history would show: request created, information requested, data provided, validation completed, approval or rejection, and communication sent. This is the sequence that support and case owners need to address questions.
The audit trail would capture: the identity of the approver, time, decision, version of the applicable rule, changes of owner, exceptional access, and any subsequent modification to the resolution. If the approval is revoked, a new entry is added with the reason; the earlier fact is not replaced.
Operational traceability would connect the form submission, validation, integration call, and delivery of the communication through a common identifier. If the message does not arrive, operations can locate the error and retries without manually reviewing the business history.
A mature decision is not about choosing one of the three. It is about using each for its purpose, defining its boundaries, and periodically checking whether real queries are answered quickly, with sufficient evidence and access proportionate to the sensitivity of the data.