

Letting a customer download their data can support everyday needs such as analysis, reconciliation, or work outside the application. But an export also creates a copy that may sit beyond the SaaS platform’s usual controls. Designing it well means deciding what it includes, who can request it, who receives the result, and how long it remains available.
The question is not simply which format to offer. Product, business, and technology teams should agree on the purpose of each export and establish controls proportionate to the sensitivity and volume of the information. The following framework helps guide those decisions without confusing an operational download with other processes.
Define the problem the export solves
An operational export lets people review or reuse specific data as part of their day-to-day work. For example, a team might need a filtered list to prepare for a review, or a file of transactions from a particular period to reconcile. Its scope should address a clear task and remain as limited as possible.
This is not the same as a report, a backup, or an extraction for a system migration. A report presents data to answer questions, often using aggregations or visualizations. A backup is designed for recovery and requires its own controls and procedures. A migration extraction may cover a broad set of entities and relationships so they can be transferred to another environment. If a self-service need starts to resemble a full extraction, consider treating it as a separate workflow, with an assessment, permissions, and support appropriate to its impact.
Before designing the interface, document the use case, the people involved, and the decision the file will support. If you cannot explain why each data group is needed, that is a reason to review the scope—not to add more fields by default.
Limit data, filters, and relationships
Specify which entities will be exported, which filters will apply, and how their relationships will be represented. An order download, for example, may need identifiers and dates, but not necessarily internal notes or data from other areas. Clarify whether the current screen’s filters are retained, whether users can choose a period, and what happens to archived or deleted records.
- Include what the task requires: leave out fields that do not add value to the stated use.
- Make the boundaries visible: explain the period, filters, time zone, or criteria that determine which records are exported.
- Define relationships: clarify whether related data is included, omitted, or represented by identifiers.
- Avoid surprises: clearly distinguish between the current view, a filtered set, and a complete export.
Excluded fields also require an explicit decision. It may be appropriate to leave out secrets, credentials, internal information, or data the requester does not need for the intended purpose. Do not assume that hiding a column in the interface automatically excludes it from the file: authorization must apply to the data set being generated.
Set permissions for the requester and recipient
Permission to view information in the application does not always imply permission to extract it in bulk. Define who can start an export based on the organization, role, and sensitivity of the data. For higher-impact information, a specific permission, additional approval, or restriction to certain roles may be appropriate. The right decision depends on context; adding friction to every download can block legitimate work without necessarily improving protection.
Consider who requests the file and who will be able to receive it separately. For a direct download, these are usually the same person. In a workflow with a different recipient, verify that the recipient is within the authorized scope and that the file will not be available to users outside the organization. Avoid automatically sending sensitive data to an address entered without validation.
The interface should explain the scope before confirmation and provide a clear way to tell when the file is ready. When an action may affect many records, a confirmation summary showing the period or number of items can help catch mistakes, provided that this information does not expose data to someone without permission.
Choose between immediate downloads and asynchronous generation
An immediate download is straightforward when the data set is small and can be prepared without blocking the application or exhausting resources. As volume or processing time increases, asynchronous generation may be more suitable: the user requests the job, receives a status update, and downloads the result when it is ready.
There is no universal threshold that works for every SaaS product. Assess the usual request size, observed processing time, system load, and user expectations. If a request takes long enough to leave the page waiting, ends in errors, or competes with important operations, those are signs that the workflow should change or the query should be narrowed.
- For small, predictable requests, prioritize a direct and understandable response.
- For longer jobs, show statuses such as pending, in progress, ready, or failed, and explain the next step.
- Avoid starting duplicate jobs when the page is refreshed or clicked repeatedly; provide a reference to the job already in progress.
- Set reasonable limits and provide a useful message when a request exceeds them, such as suggesting that the user split it by period.
Asynchronous processing does not remove the need to control access. The user must authenticate to check the status and retrieve the result, and the system should verify again that the user remains authorized when appropriate.
Protect the file and limit risk
The result needs its own controls: it may contain a concentration of information that is not gathered together on any single screen. Use temporary storage with restricted access and set an expiration period that fits the use case. Tell users when the file will no longer be available and avoid keeping copies longer than needed to complete the task.
Access should preferably require authentication and a permission check tied to the organization. If download links are used, treat them like credentials: limit how long they remain valid, avoid exposing sensitive information through them, and consider the risk that they may be forwarded. A hard-to-guess link alone is not a substitute for proper authorization. Also avoid exposing file names or error messages that reveal unnecessary data.
Set limits that reduce accidental errors and abuse without preventing normal operations. Depending on the use case, these may include a maximum number of records, request frequency, concurrent jobs, or splitting exports by period. A control may be too restrictive if users with a legitimate need cannot complete routine tasks; if it is too permissive, unusual volumes, repeated retries, or extractions outside expected patterns may appear. Review limits using operational data and feedback, rather than arbitrary figures.
Log, validate, and review before release
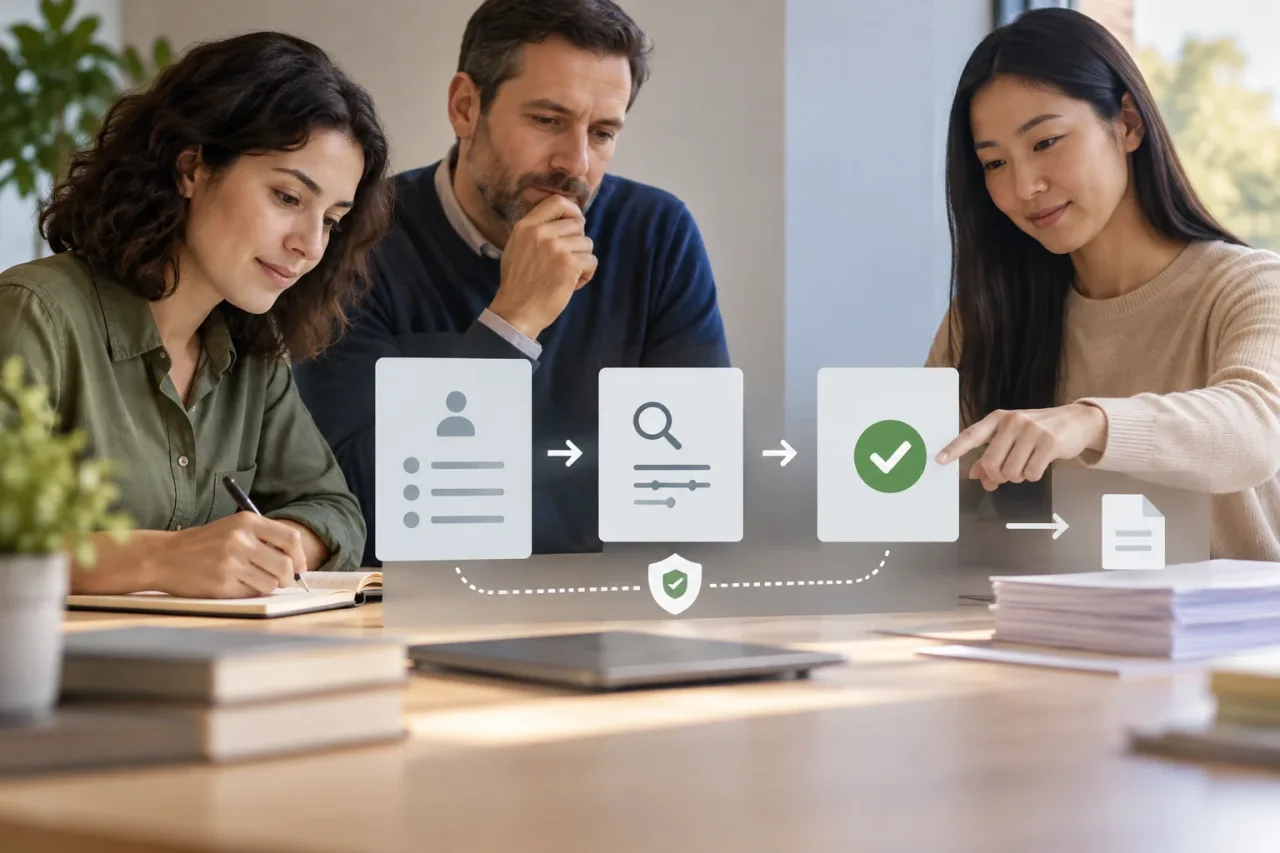
Record enough information to investigate an incident: who requested the export, which organization they belong to, when it started, what scope or filters were applied, and whether it succeeded or failed. Avoid putting file contents or unnecessary sensitive data in logs. Traceability should make it possible to reconstruct the action without creating another copy of the data.
Also check that the file is usable. Validate the offered format, text encoding, headers, field names, empty values, and consistency of relationships. A file that is generated correctly from a technical standpoint but remains ambiguous can lead to interpretation errors and support requests. Explain available formats and any relevant limits; do not assume all users will open the result with the same tool.
Before release, review this checklist with product, technology, and the people responsible for access to the information:
- Is the purpose documented and distinguished from reports, backups, and migrations?
- Have the entities, filters, relationships, and excluded fields been defined?
- Are organization and role checked, along with a specific permission where needed?
- Is it clear who requests the file and who receives it?
- Do the experience and limits match expected size and processing time?
- Does the file have controlled access, an expiration period, and a deletion policy?
- Are requests, results, and errors logged with proportionate traceability?
- Have permissions, edge cases, formats, and error messages been tested?
A well-designed export feature makes its boundaries clear and lets people complete legitimate tasks without opening a broader access path than necessary. If the use case requires complete data, complex relationships, or delivery to third parties, the right choice may be to create a separate process rather than stretch an operational download into an extraction without adequate controls.