

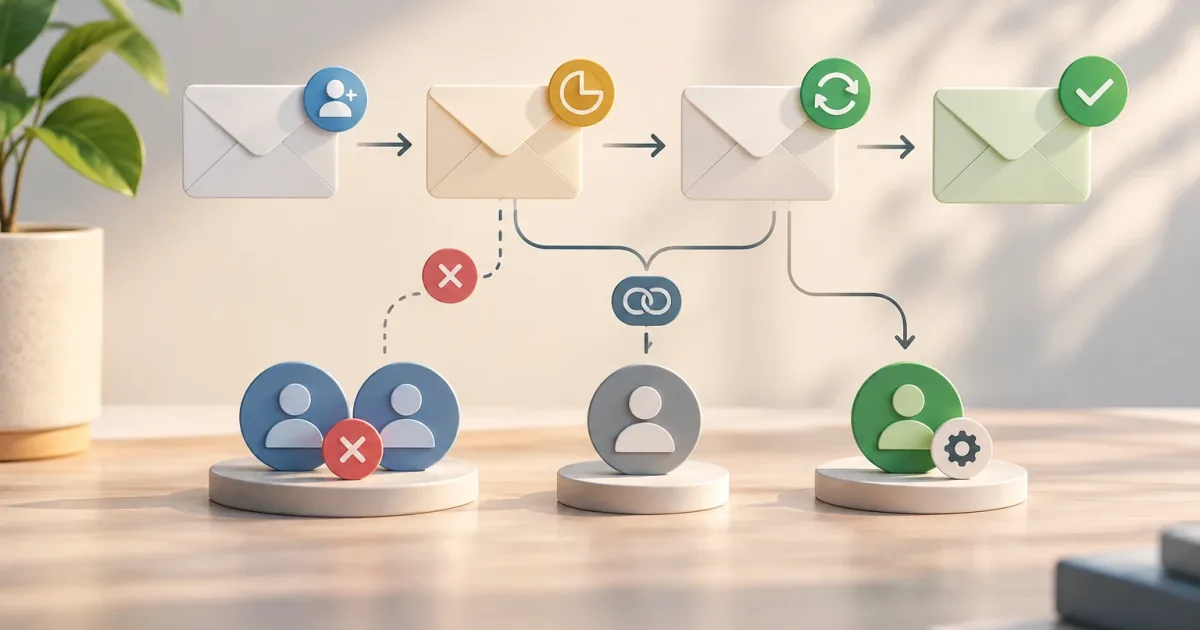
A user invitation may look like an email with a link, but in a B2B SaaS product it is an identity and organization membership flow. If the product does not define what happens when a link expires, is resent, or reaches someone with an existing account, the team ends up handling exceptions manually and users receive outcomes that are hard to understand.
The product decision is to model the entire lifecycle, not just the act of sending an email. Treat the invitation as a pending request for an email address to join an organization, separate from the user account and the permissions they will have after joining. This distinction helps create a predictable, auditable, and secure process.
Model invitations with explicit states and transitions
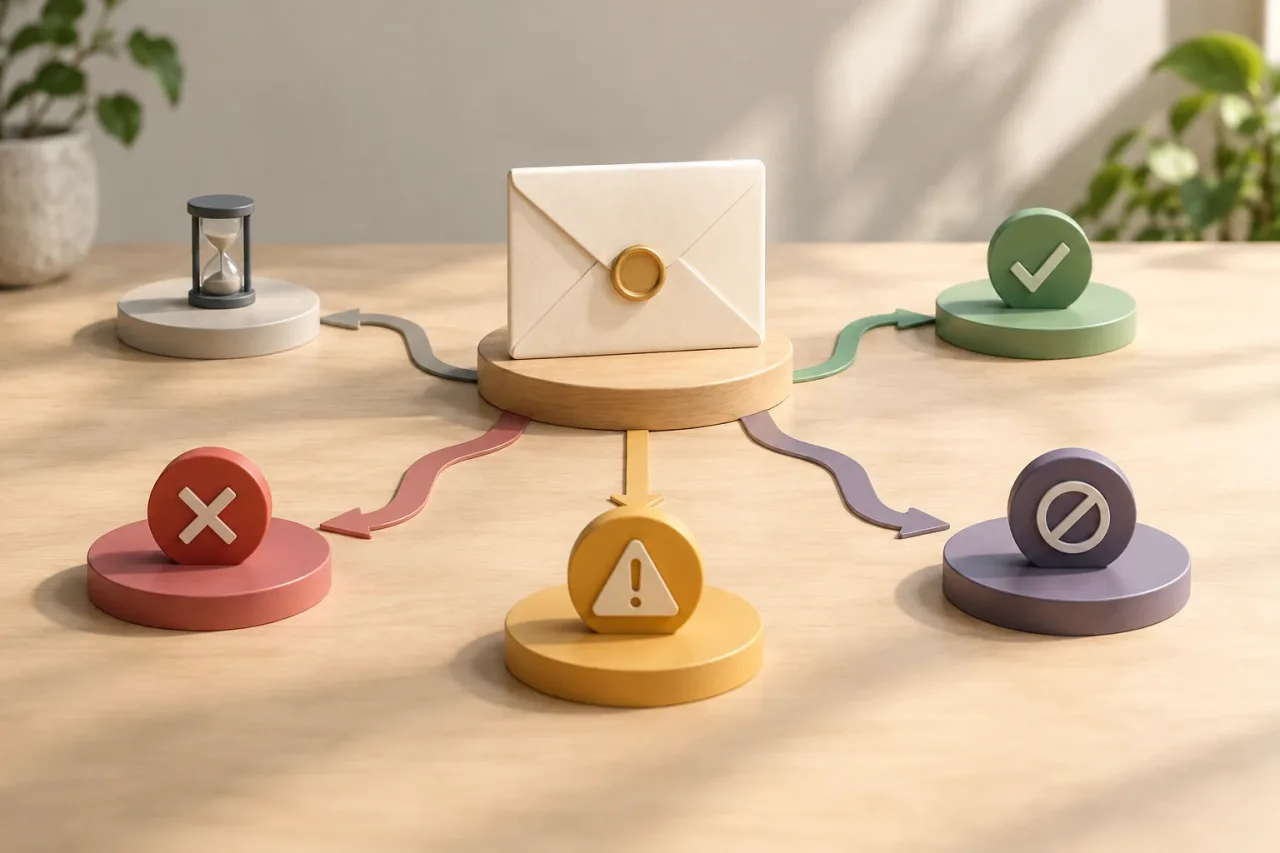
Start by defining the states your product needs. A common model includes pending, accepted, expired, and revoked. If email delivery failures can be observed, record that outcome separately or add an operational state such as “delivery failed.” Do not turn every delivery problem into a business state if the user can still accept the invitation.
Specify which actions trigger each transition. A pending invitation can be accepted, revoked, or expire; an expired invitation can be replaced with a new one; and an accepted invitation must not be accepted again. Revocation must make the link unusable even if the original message is still in the recipient’s inbox.
- Identify the object: store the organization, invited email address, who created the invitation, and when.
- Define the outcome: record the acceptance and the identity that completed the process.
- Avoid ambiguous states: “email sent” does not necessarily mean “invitation accepted,” and it does not guarantee that the message was read.
This separation also makes the administration screen easier to explain: who is pending, since when, and what the administrator can do next.
Choose expiration based on risk and user experience
Expiration limits how long an invitation link can be used. An invitation that remains valid for too long extends the period during which a forwarded or exposed link can still be used. One that expires too quickly creates friction, especially if the invitee checks their email days later. There is no universally correct duration; it depends on the risk, the type of organization, and how much control the administrator needs.
Define consistently what happens when an invitation expires. The clearest option is usually to say that the invitation is no longer valid and provide a way to request another one. If the user is signed in, you can direct them to the organization’s administrator. Do not present an expired invitation as if the account were locked: these are different situations.
In the inviter’s interface, show the expiration date or expired status, and allow a new invitation to be created if the inviter is authorized. Also decide whether the new invitation retains the original recipient and intended role or whether the administrator must review them. Expiration must be enforced by the server, not just shown as a visual timer: the system must check it when the invitation is accepted.
Design resending and email changes without reviving old links
Resending can mean two different things: sending the same link again or issuing a new one. If the link is retained, its expiration date and token remain unchanged. If a new link is generated, explicitly define whether the old one is invalidated. To avoid multiple active routes to the same invitation, it is usually simpler to revoke the previous token when issuing a new one.
The inviter needs confirmation that the action succeeded and a clear indication if delivery fails. Avoid letting a resend button create separate invitations every time it is clicked: apply an idempotency rule or check whether an equivalent pending invitation already exists. It is also useful to prevent accidental repeat sends without blocking a legitimate new attempt.
If the email address changes, treat the change as sensitive. The clearest solution is usually to revoke the invitation sent to the old address and create another for the new one. Do not silently change the recipient while keeping a link that has already been sent: whoever controls the old inbox could retain access to the process. Record the change so the organization can understand what happened.
Handle duplicates and existing accounts
Before creating an invitation, define what counts as a duplicate. A practical rule is to consider the combination of organization and normalized email address, using the same normalization conventions throughout the system. Do not apply aggressive transformations to email addresses: some equivalences that may seem obvious are not universal. Retain the address entered by the user for display and delivery.
If a pending invitation already exists for that organization and email address, offer a useful action: show its status, resend it, or revoke and replace it, depending on the actor’s permissions. Do not create a second entry that leaves administrators unsure which invitation is valid.
If the email belongs to an existing account, the invitation can add that identity to another organization, provided the person authenticates with the correct account and accepts the invitation. An existing account does not mean membership in every organization. If multiple accounts could be associated with the same email, do not link them automatically without a verification mechanism and a defined identity rule.
Protect the link and verify who accepts it
The link should work like a temporary credential. Use a token that is difficult to guess, tied to a specific invitation, and checked for expiration on the server. Do not include sensitive information in the URL, and avoid exposing the token in logs, analytics, or third-party pages. OWASP guidance on secure credential and session management can serve as a reference when reviewing the design.
When the link is opened, show enough context for the person to understand which organization they are joining and which email address was invited. Before completing acceptance, verify that they control that email. If they are already signed in with a different identity, explain the conflict and ask them to switch accounts or complete verification rather than linking the identities for convenience.
Acceptance should be an atomic operation: check that the invitation is still pending and valid, confirm the identity, create the membership, and mark the invitation as accepted. If two requests attempt to use the same link at the same time, only one should complete the change. A subsequent visit can say that the invitation has already been used without granting access again.
Define what happens when permissions change or an invitation is revoked
An invitation can include an initial role or a reference to the permissions that will apply upon acceptance. Decide whether those permissions are fixed when the invitation is sent or looked up at acceptance. Fixing them makes the original offer explicit; looking them up later reflects recent changes but can surprise the inviter. In either case, communicate relevant changes and avoid expanding permissions without a deliberate decision.
If an invitation is revoked before acceptance, its link must stop working, and the invitee should see a neutral message explaining that they can no longer complete the process. Do not reveal unnecessary information about the organization. If the role or email changes, record who made the change and when, especially when several people administer the organization.
Test edge cases and monitor the flow
Tests should cover the happy path as well as transitions that commonly generate support requests. At a minimum, include acceptance before and after expiration, resending when an old link exists, revocation, double-clicks, repeated invitations, existing accounts, a session signed in with another email, and a role change while an invitation is pending.
- Check that a used, expired, or revoked token does not grant access.
- Verify that an email delivery failure does not mistakenly change the acceptance status.
- Confirm that retries do not create duplicate memberships or invitations.
- Review whether messages explain the next step without revealing other people’s data.
In production, monitor counts of pending, expired, revoked, and accepted invitations, along with delivery failures and time to acceptance. Interpret these signals together: many expired invitations may point to unsuitable time limits or emails that are not reaching recipients; many resends may indicate that the message is unclear or the flow is getting stuck. A metric alone does not prove the cause, so pair it with support feedback and user experience testing.
The design rule that connects the entire flow is simple: every invitation must have a recipient, a state, a time limit, and an unambiguous outcome. Once those decisions are documented, the team can handle exceptions without confusing invitations with accounts, memberships, or general permissions.