

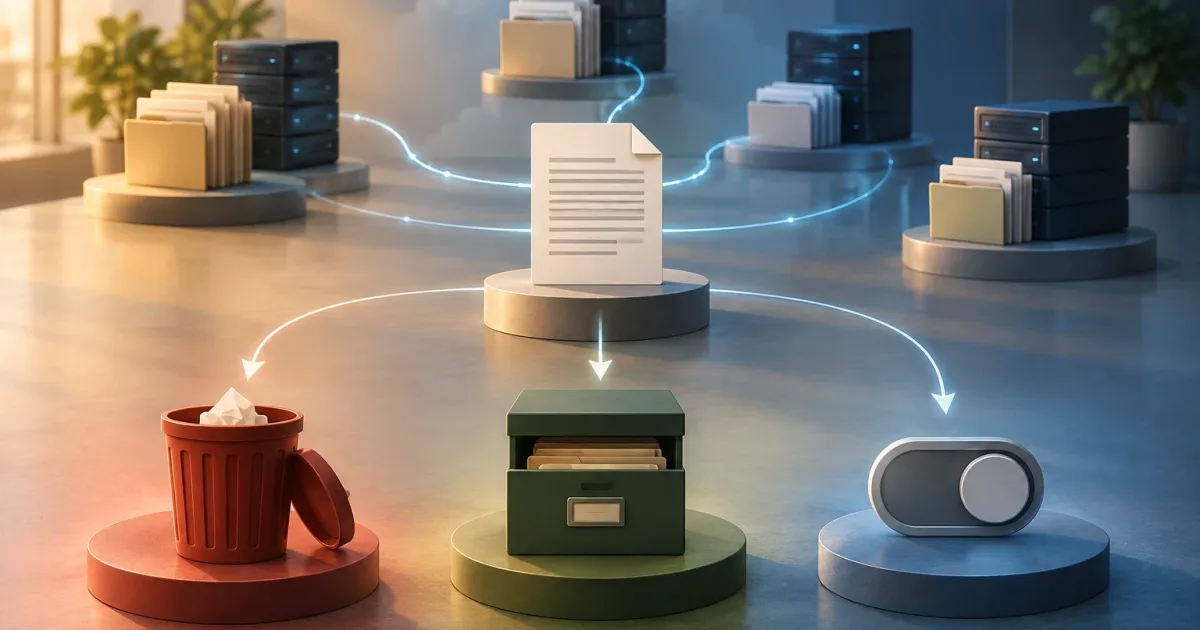
A user deletes a record in one application and finds it again hours later because another application synchronized it. This is rarely an isolated deletion problem. It is a disagreement between systems about what action took place, what it means, and which systems must respect it. Resolving the issue requires agreeing on business and integration rules before connecting the applications.
The practical question is not only how to synchronize deletions between systems. It is also whether a record should disappear, be hidden, remain available for audit, or continue to support pending processes. This article distinguishes those choices and outlines how to communicate them, prevent unintended restoration, and handle exceptions.
Why a local deletion does not always reach connected systems
An integration may copy new and changed records without transmitting removals. For example, if it periodically queries available records and sends only those it finds, a record that no longer appears at the source will not necessarily generate a message to the destination. The receiving system cannot tell whether the record was never sent, the query failed, or the record was deleted unless an explicit rule makes that clear.
The problem also arises when one application retains a record while another physically deletes it. If a later synchronization republishes the retained record, the destination may recreate it. “Last updated” logic is not always enough either: the deletion may not have a timestamp or version that can be compared with incoming changes.
Before designing a solution, identify which applications can create, edit, or remove the record, which system is authoritative for each data item, and what it means for that record to become unavailable. For two-way synchronization, also decide what happens if one application deletes a record while another edits it. Without that decision, the system cannot resolve the conflict reliably.
Deleting, archiving, and deactivating are different actions
- Physical deletion: The record is removed from the system’s active structure. It may no longer be available through ordinary functions, although backups, technical logs, and retention policies may follow their own rules. Do not assume this automatically removes every trace.
- Archiving: The record is retained but removed from routine work, such as default views. This can be useful when history or context must remain available. Define whether connected systems receive an “archived” state or simply stop displaying the record.
- Deactivation: The record remains, but no longer participates in an operation. A deactivated product, for instance, may remain associated with earlier orders while no longer being offered for new sales. The exact meaning depends on the process; “inactive” has no universal definition.
It is also useful to distinguish a requested removal from a correction. Restoring a record deleted by mistake may be appropriate; restoring a record that was permanently removed through synchronization is a failure. Model these actions separately when they trigger different permissions, retention requirements, or operational effects.
Choose the meaning based on the business process
Start with the observable outcome, not the function available in an interface. Ask what each team and system should be able to do after the action. Should a new operation be allowed to use the record? Should it remain searchable in historical records? Do invoices, orders, cases, or reports depend on it? The answers may lead to different choices for different record types.
A practical guideline is to use deactivation when a record remains a valid reference but must not start new operations; archiving when it needs to be retained but removed from routine activity; and physical deletion only when applicable policy and dependencies allow it. This is not a mandatory hierarchy: the decision should reflect business needs, retention requirements, and the actual capabilities of the systems.
Document the rule in verifiable terms. Instead of saying “synchronize the removal when a record is deleted,” specify what action initiates it, which systems receive it, what changes in each system, and whether the action can be reversed. Agree on authority too: if only one system can decide to remove a record, changes in other systems should not reactivate it without an authorized action.
What signal should travel through the integration
The integration needs an unambiguous representation. One option is to transmit a removal event when the action occurs. Another is to send an explicit state, such as active, archived, or deactivated, with each relevant exchange. A deletion marker can also be used to retain the record while making its removed status recognizable in later synchronizations.
The right choice depends on how the exchange works. Events communicate a change when it happens, but systems must handle retries, duplicates, and out-of-order messages. An explicit state makes it easier to compare current status, but queries must include inactive records or their removal markers. If the source simply omits a deleted record, the receiver does not have enough information to distinguish removal from temporary absence.
Whatever the mechanism, define a stable identifier for matching the record across systems, the state or action type, the time or version of the change, and the source system. The receiver should be able to process the same signal more than once without creating contradictory effects. If applications use different states, agree on an explicit mapping; do not assume that “archived” in one system means “deleted” in another.
How to prevent synchronization from restoring records
The main safeguard is to retain and propagate removal information long enough for the other systems to receive it. If the source physically deletes the record before the integration detects it, the only evidence that it existed may disappear too. A removal marker or event record retained until propagation is confirmed avoids relying on absence as a signal.
The destination should recognize removal as a state, not as a temporary instruction that disappears after processing. If it later receives an older copy marked active, it needs a precedence rule—for example, comparing versions or change times and rejecting older data. Where restoration is allowed, require an explicit, authorized reactivation action rather than inferring it from an ordinary update.
Plan for recovery after interruptions as well. A restarted synchronization must be able to detect changes that occurred while it was stopped. Agree on how signals are retried, how already-applied messages are identified, and how errors are reviewed. A report of pending removals and alerts for recreated records can reveal problems before they become discrepancies that are difficult to trace.
References, pending processes, and exceptions
A record may be linked to other data that must be retained: an order, transaction, support case, or change history. Physical deletion could break a reference or make a past operation difficult to interpret. In such cases, the receiving system may need to retain a minimal version or mark the record as unavailable for new operations. The decision must respect applicable policies and each system’s capabilities; do not assume every system supports the same kind of removal.
Review in-progress records separately. If an approved request, a product on an order, or an active task is deactivated, should it be cancelled, completed, or retained without allowing new operations? A general rule may not be enough: define which process takes precedence and who can resolve the exception. If an application does not support deletion, assign it a compatible removal state and document what data it retains and who can access it.
Corrections need a separate path. An erroneous removal may need to be reversed, but reactivating a record should not erase the removal history or conceal who made the decision. Separating “correct a removal,” “restore,” and “reactivate” helps maintain an understandable audit trail and prevents an automated process from reopening records by accident.
Pre-launch checklist
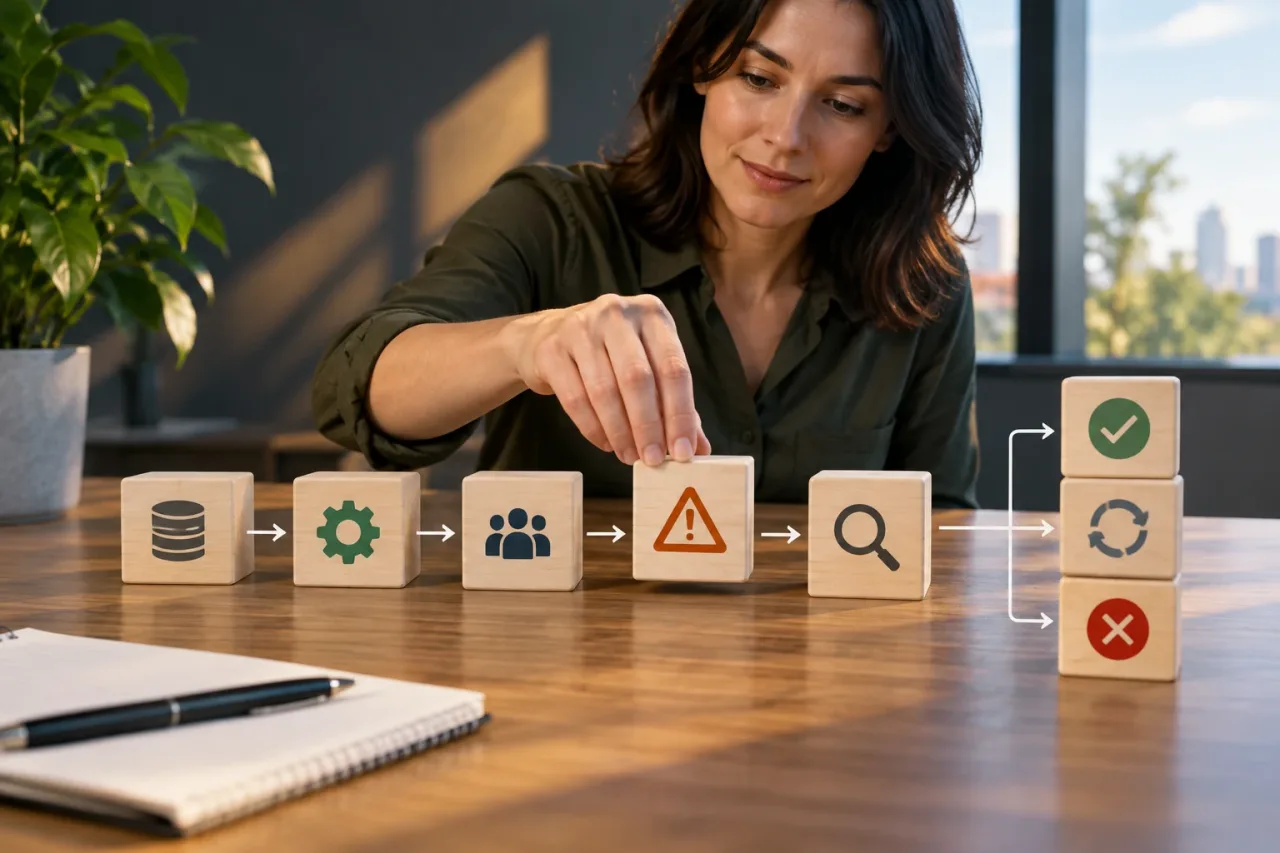
- Define the scope: Identify record types, participating systems, and the actions that can initiate removal.
- Agree on meanings: Specify what deleting, archiving, and deactivating mean for each business process.
- Assign authority: Establish who can remove a record and who can restore or reactivate it.
- Design the signal: Choose an event, state, or removal marker, and define identifiers, versions, and duplicate handling.
- Protect dependencies: Check references, history, pending processes, and systems that do not allow deletion.
- Test adverse scenarios: Include repeated messages, interrupted synchronization, concurrent changes, older data, and authorized restorations.
- Prepare monitoring: Agree how to review pending removals, failures, recreations, and discrepancies, and who responds to each alert.
The right choice is not always deletion. It is to communicate a clear business intent, retain necessary information, and ensure that all connected systems interpret it consistently. When the rule can be expressed as states, responsible parties, exceptions, and observable tests, synchronization is far less likely to turn a removal into an unexpected addition.