

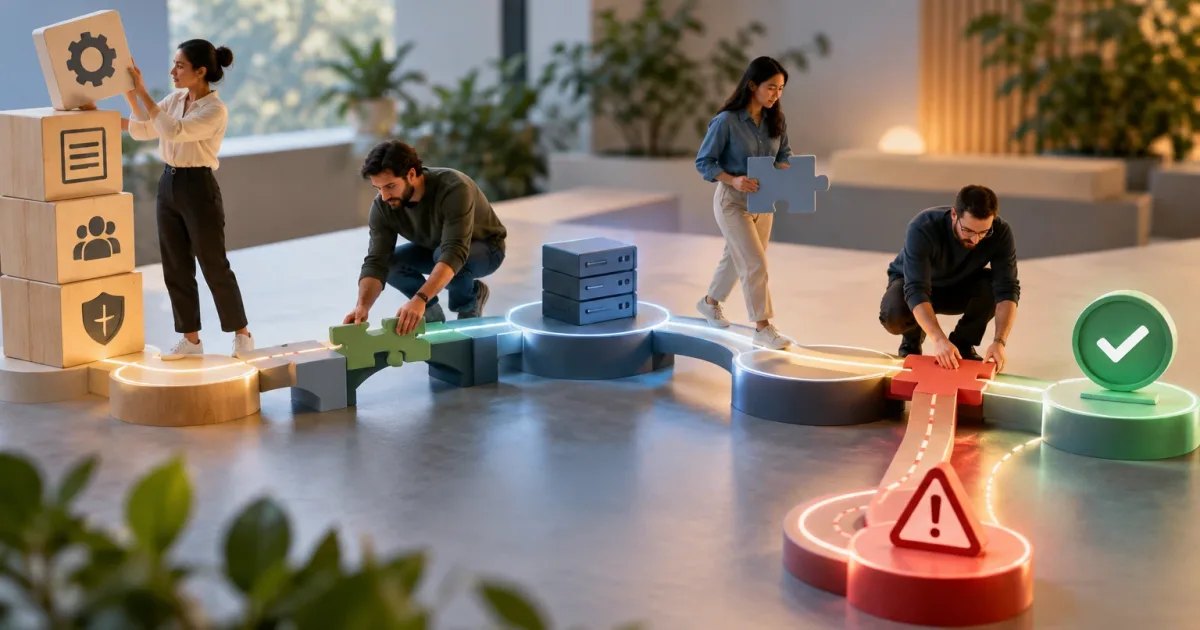
A screen can work and still fail to solve the problem that prompted its development. It may accept data that should be rejected, calculate an incorrect amount, or leave an operation incomplete in a connected system. That is why business rule-based acceptance testing goes beyond checking visual controls: it verifies whether a process produces the expected outcome for people and the organization.
The key is to start with concrete operational decisions and turn them into scenarios that can be verified using data, results, and evidence. This gives product, business, QA, and technology teams a shared, practical definition of what it means to accept a change.
Checking a screen is not the same as validating a rule
An interface test can confirm that a button appears, that a form accepts input, or that a message is displayed. These checks may be necessary, but on their own they do not prove that a business policy is being followed. To do that, you need to trace the relationship between a condition and its consequence.
For example, the question is not just whether a request can be submitted. You also need to know which conditions determine approval, what happens when information is missing, and what status should be assigned to cases requiring review. A rule may be applied in a screen, a service, or a later manual process; acceptance testing should verify the relevant outcome without assuming where the rule is implemented.
A useful testable rule expresses an observable decision: given certain input conditions, the process must produce an identifiable result. If the rule depends on interpretation, clarify it before writing the test case. A test should not be the first place where the meaning of a policy is discovered.
Identify rules, actors, data, and outcomes
Before writing scenarios, bring together the people who know the process and those who implement it. The aim is to describe what decision is made, who is involved, and what information changes that decision. You do not need to document every system detail, but you do need to make explicit the conditions that affect the outcome.
- Actor: who initiates or reviews the operation, such as an end user or a supervisor.
- Conditions: rules, permissions, previous states, and constraints that affect the decision.
- Input data: values needed to run the scenario, including values that may be missing or invalid.
- Expected outcome: the final state, an action that is allowed or denied, a calculation, a notification, or a task that must be generated.
- Evidence: how the outcome will be checked, for example, through a recorded status, a visible response, or an activity in the relevant system.
Record open questions and assign someone to resolve each one. If a rule has exceptions, identify who can authorize them and how that authorization is documented. Do not turn a team assumption into an unspoken requirement.
Turn rules into clear, observable scenarios
Write each scenario with enough context for another person to run it and evaluate the outcome. A simple structure is: given a set of conditions, when an action is performed, then a specific outcome is expected. The format matters less than the precision: inputs and expectations must be explicit.
- Describe a recognizable business situation, not a sequence of clicks without a purpose.
- Specify the data and initial state needed to reproduce it.
- State which action starts the decision or process.
- Define the outcome that should be observed and where to verify it.
A criterion such as “the system handles the request correctly” cannot be approved consistently. A verifiable criterion instead specifies which requests are accepted, which are rejected or routed for review, and what status is recorded. If the expected outcome can be interpreted in several ways, the criterion still needs work.
Avoid combining too many rules in one scenario. When it fails, the team should be able to identify which behavior does not match what was agreed. At the same time, do not duplicate tests that verify the same outcome with equivalent data unless they add distinct coverage.
Cover boundaries and exceptions without multiplying test cases
The typical case helps confirm the main workflow, but it is rarely enough. Rules often produce different outcomes at a boundary, when data is missing, or when conditions are combined. Start by asking which data could change the decision and what happens immediately before, at, and after the boundary.
Prioritize variations that change the process outcome: permitted and prohibited values, different permissions, incompatible states, duplicates, or incomplete information, provided they apply to the actual rules. If several conditions are independent, you can select representative combinations rather than testing every possible combination. If a combination could change the decision, it should be covered.
It is also useful to distinguish a business exception from a technical error. A request denied under a policy may be a correct outcome; an interruption that prevents the state from being saved is a different situation. Agreeing on this distinction helps prevent a change from being rejected because a rule worked as intended, or an operational failure from being accepted as a planned exception.
Validate end-to-end workflows across systems
When several applications or teams are involved, check the end-to-end workflow from the event that starts the process to the outcome the operation needs. It is not enough to verify that one system sent information: confirm that the receiving system interpreted it and that the final state is consistent.
Identify handoff points, owners, and observable signals. For example, what happens if the second system is unavailable? Is the operation retried? Does it remain pending for review? How is duplicate processing prevented? The answers should reflect the agreed behavior, not assumed capabilities. If the workflow cannot be tested end to end in an available environment, document which part is tested separately and what uncertainty remains.
A brief process map helps distinguish acceptance checks from technical tests of individual components. Acceptance focuses on the operational consequence; component and integration tests provide other forms of evidence, but they do not replace validation of the business outcome.
Agree on evidence, responsibilities, and decisions
Before execution, agree on who prepares the data, who runs each scenario, and who makes a decision when there is a discrepancy. Business stakeholders should confirm that the outcome follows the rule; product coordinates scope and priorities; QA can help with coverage and record results; and technology teams can help diagnose behavior. Responsibilities may vary, but they should not be left implicit.
Define what counts as sufficient evidence and how it will be recorded: the scenario, data used, observed outcome, approval status, and any issue. There is no need to collect sensitive information that does not contribute to the check. Use representative, authorized data, and prepare a controlled alternative when using real data is not appropriate.
The decision should also be explicit. A failure involving a critical rule may block acceptance; a minor discrepancy could be accepted with an agreed action if the people responsible have the authority to decide. In every case, record the impact, owner, and next step. Do not hide an outstanding condition behind an ambiguous “approved” status.
Common mistakes and a checklist
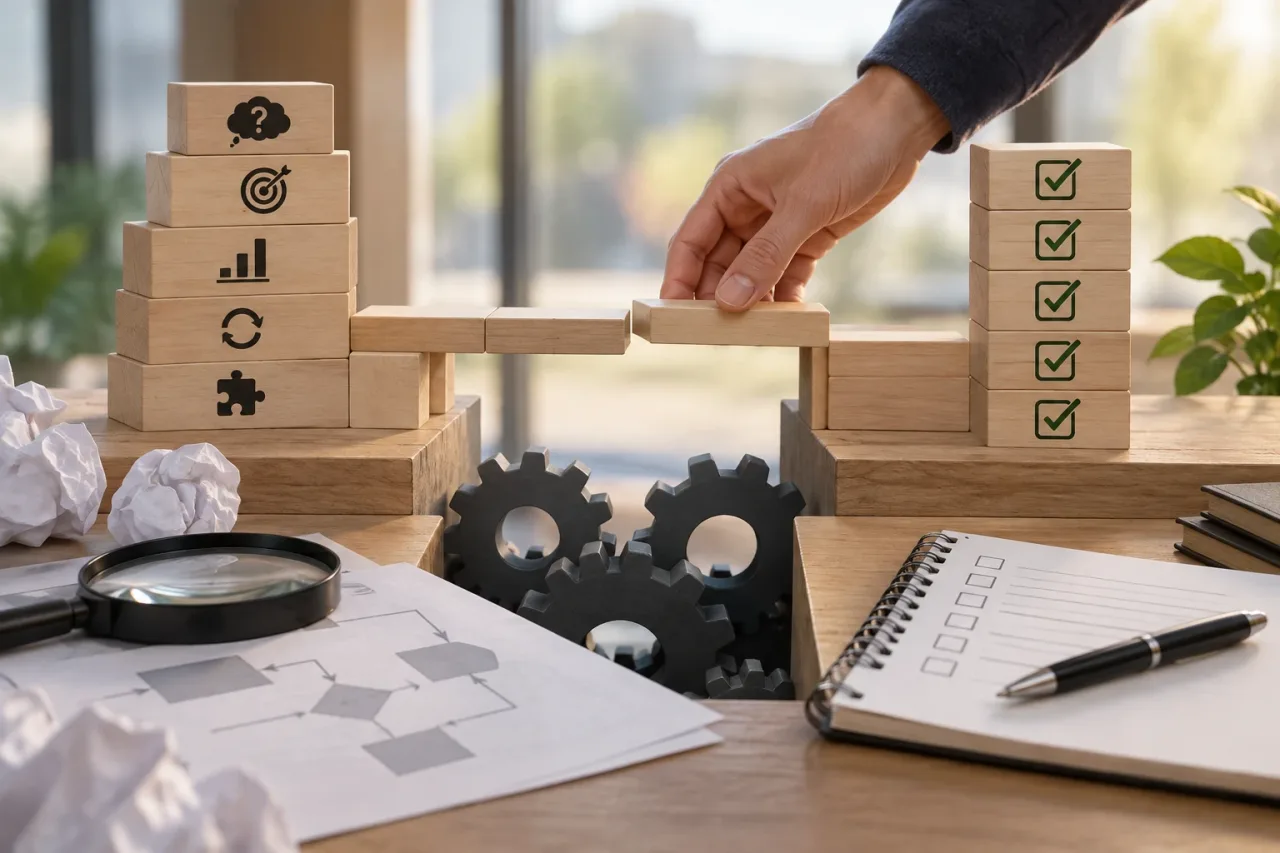
The most common problems are vague criteria, scenarios focused only on the ideal case, data that does not represent the process, and tests that repeat existing checks without verifying a new decision. It is also risky to validate each system separately and assume the entire workflow will work automatically. The answer is not to add test cases indiscriminately, but to review which rule, exception, or handoff still lacks clear evidence.
Before the acceptance session, check the following:
- Have the rules and their exceptions been confirmed by the people responsible?
- Does each scenario specify initial conditions, data, an action, and an observable outcome?
- Are the main workflow, relevant boundaries, and expected denials covered?
- Do cross-system cases check the final state and relevant handoff failures?
- Is it clear who runs the tests, who provides evidence, and who makes the final decision?
- Are discrepancies, outstanding risks, and agreements recorded?
Effective acceptance testing does not aim to prove that everything works in every circumstance. It aims to provide sufficient evidence that the relevant rules are followed in representative scenarios and that important exceptions have an agreed response. This approach reduces ambiguity and gives teams a stronger basis for accepting, correcting, or postponing a change.